LazyOwn MCP Server
 by grisuno
837 CLI commands. Multi-operator C2. 153 MCP tools for AI agents. The First OSS C2 with Linux native c BOF support + built-in YARA/Nuclei marketplaces.
LazyOwn is an open-source mcp server by grisuno, written mainly in HTML, with 300 GitHub stars and the AGPL-3.0 license. Its code was last updated Nov 1, 2026.
LazyOwn RedTeam Framework with AI agents, Linux BOF beacon, YARA+Nuclei marketplace
<img width="862" height="862" alt="image" src="https://github.com/user-attachments/assets/6157c084-c743-4042-bd91-f8d2cc6a194c" />




872 CLI commands. Multi-operator C2. 153 MCP tools for AI agents. The First OSS C2 with Linux native c BOF support + built-in YARA/Nuclei marketplaces.
Install in one command
curl -fsSL https://raw.githubusercontent.com/grisuno/LazyOwn/main/bootstrap.sh -o /tmp/bootstrap.sh \
  && bash /tmp/bootstrap.sh
| Try in 60 seconds (no install) | Golden path (every engagement) | One-command auto-pwn |
|---|---|---|
docker run -it ghcr.io/grisuno/lazyown:latest | ping > lazynmap > auto_populate > facts_show > recommend_next | auto_loop --target 10.10.11.5 |
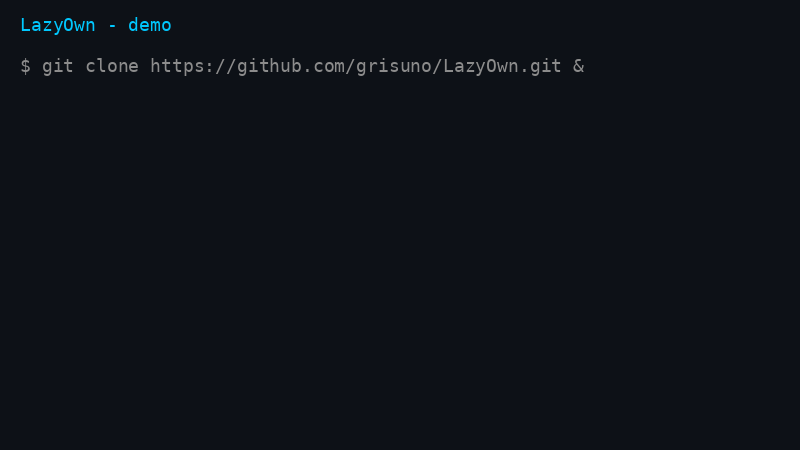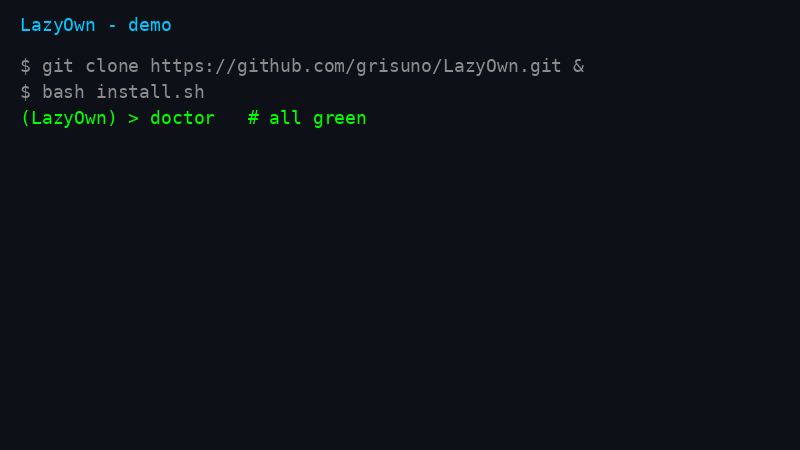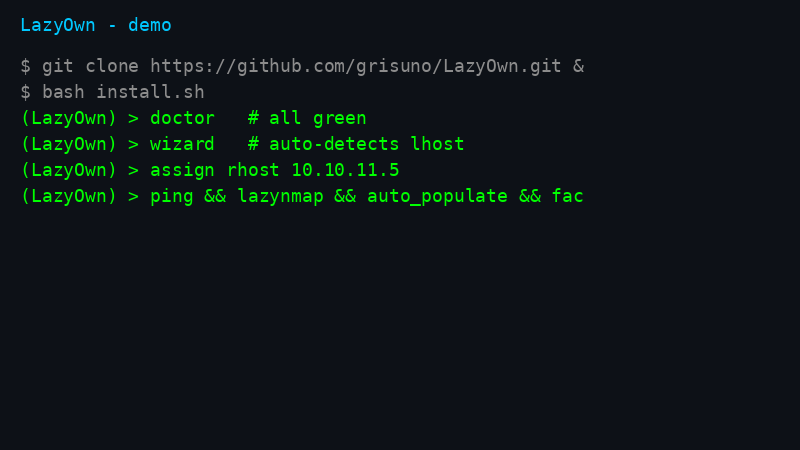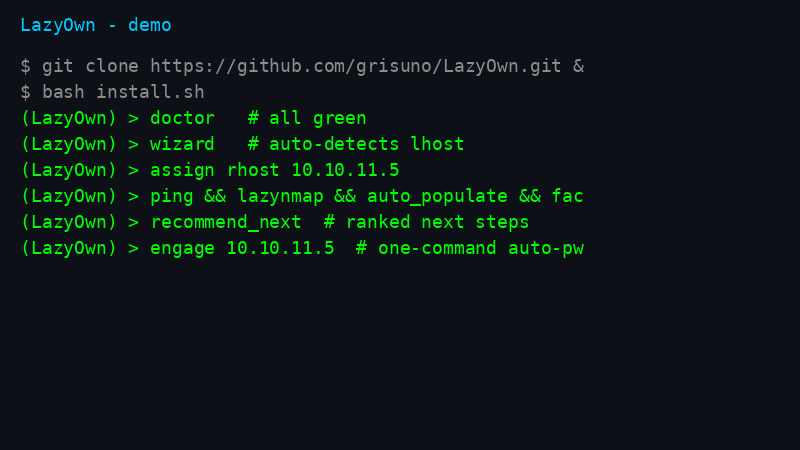
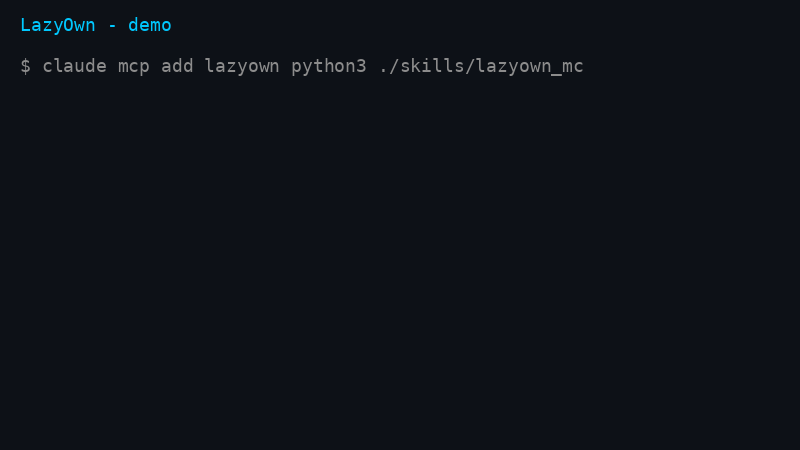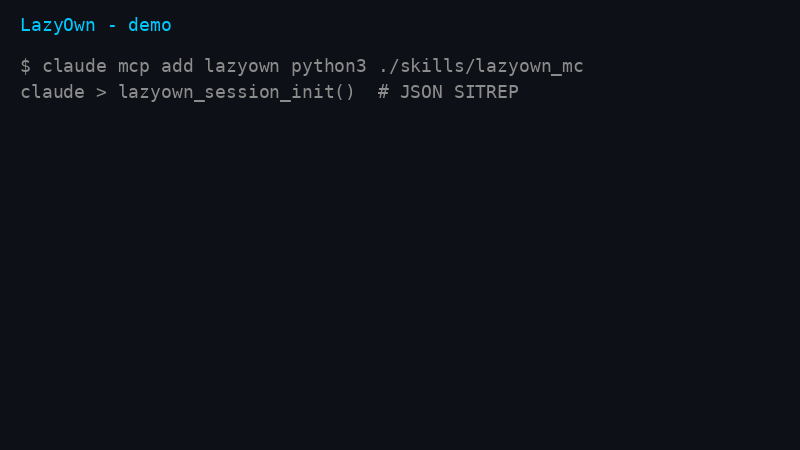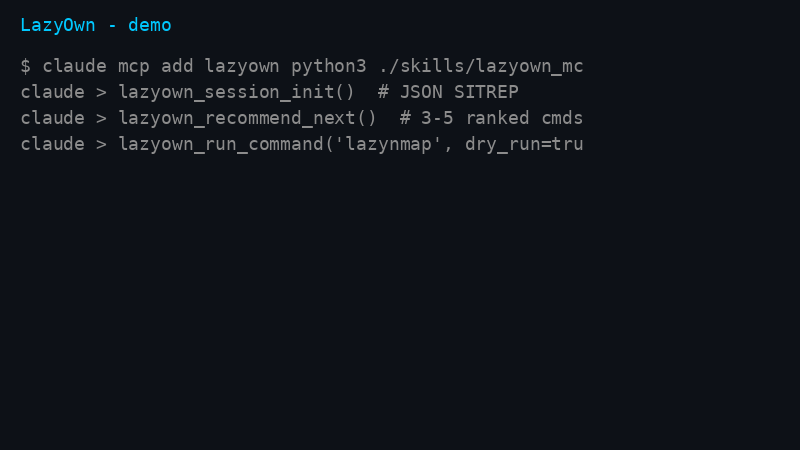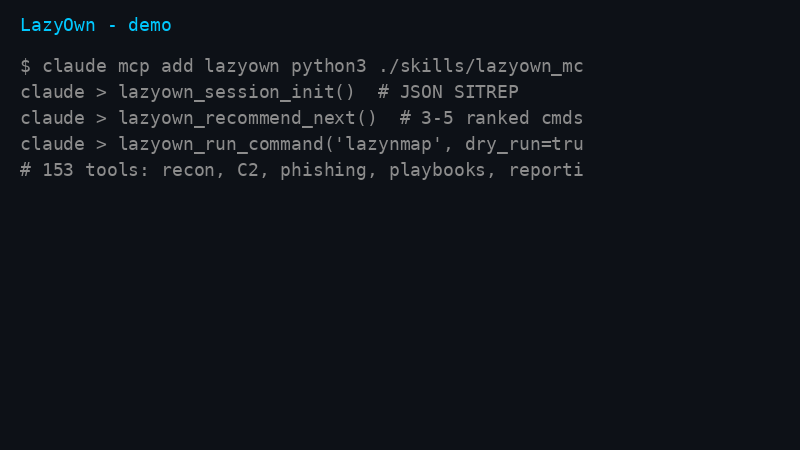
More demos
| First 7 commands | Recon loop |
|---|---|
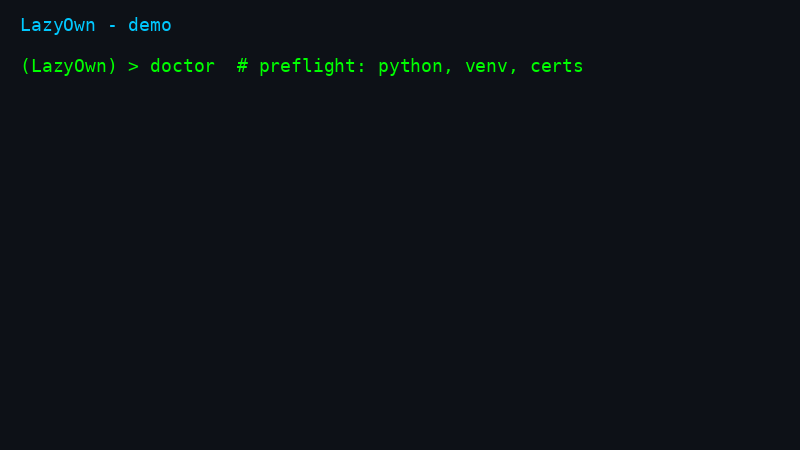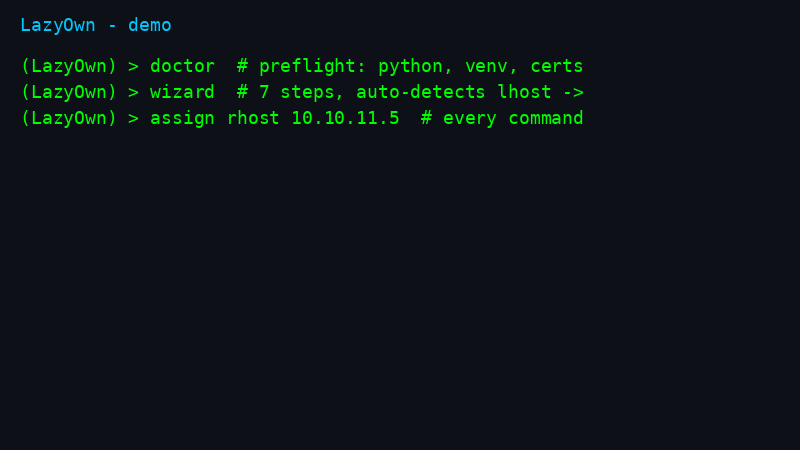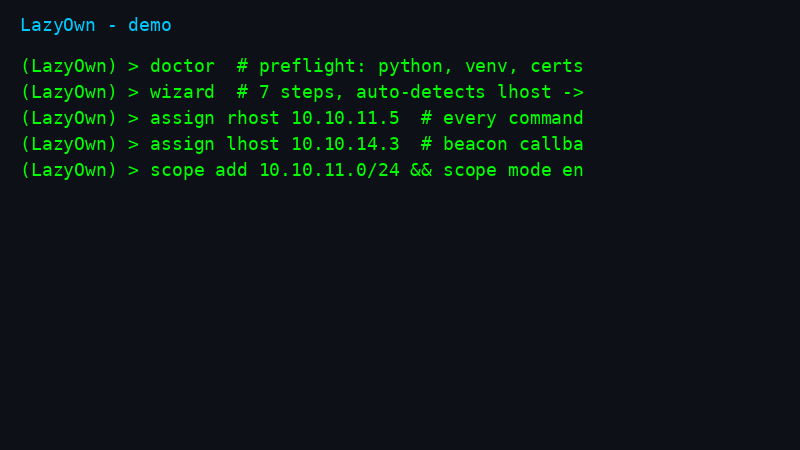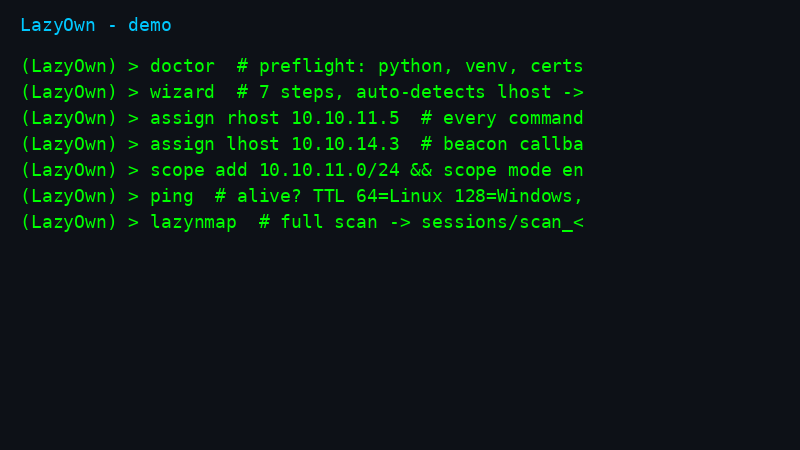 | 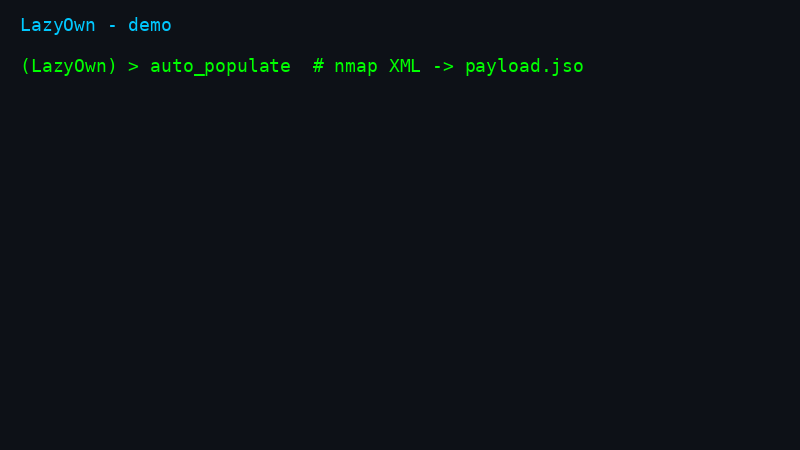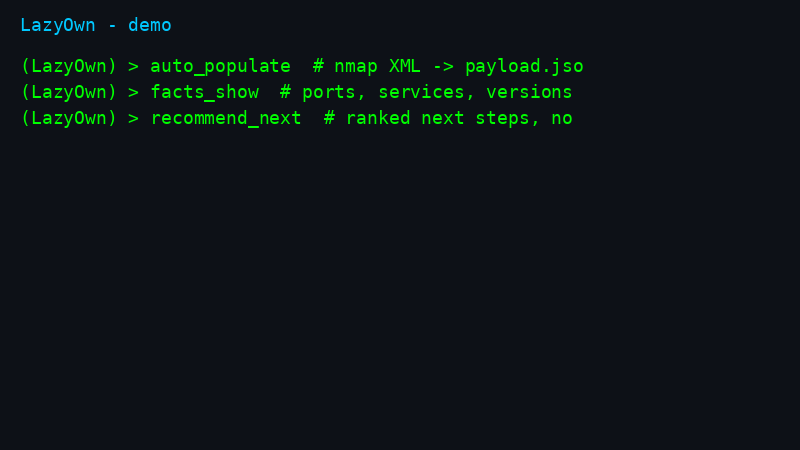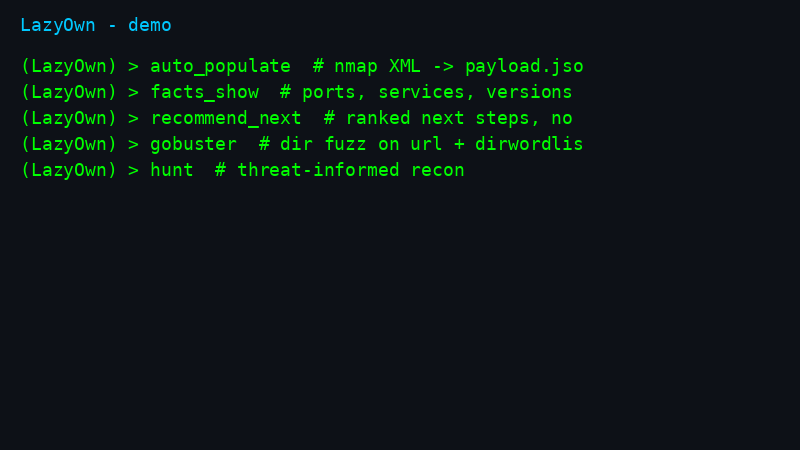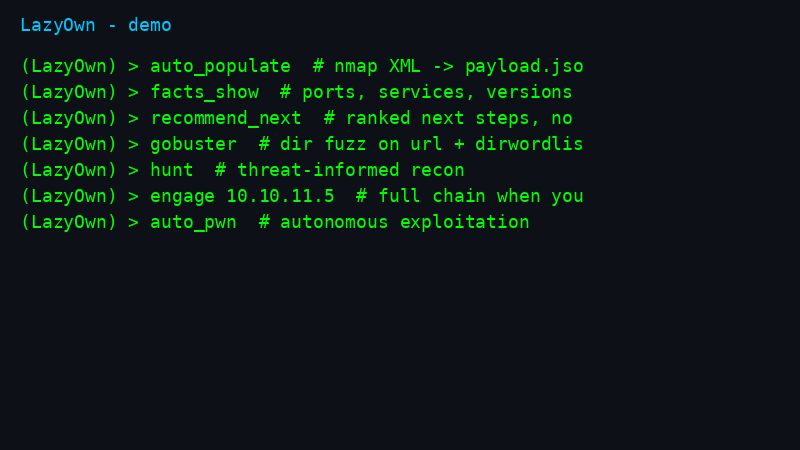 |
| C2 from CLI | Issue commands to beacons |
|---|---|
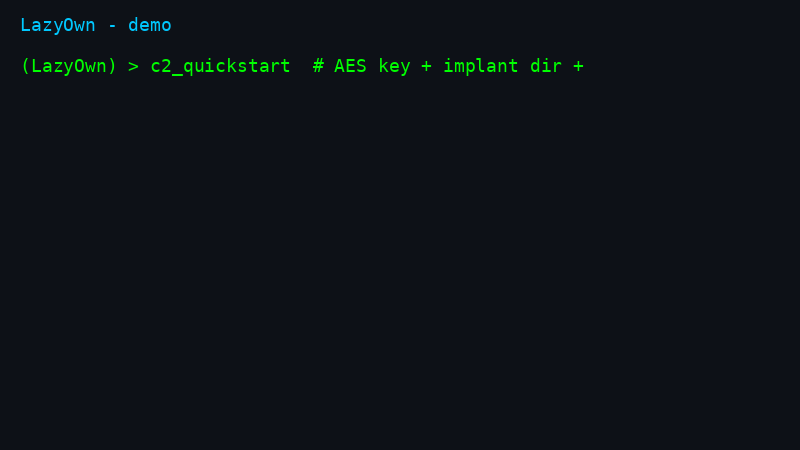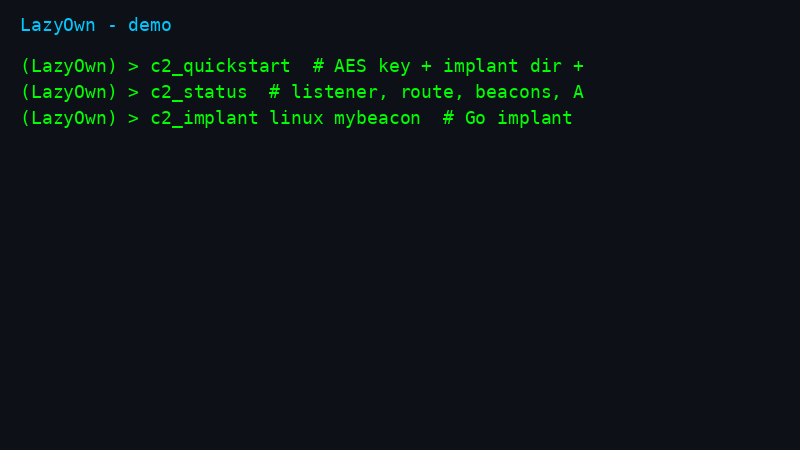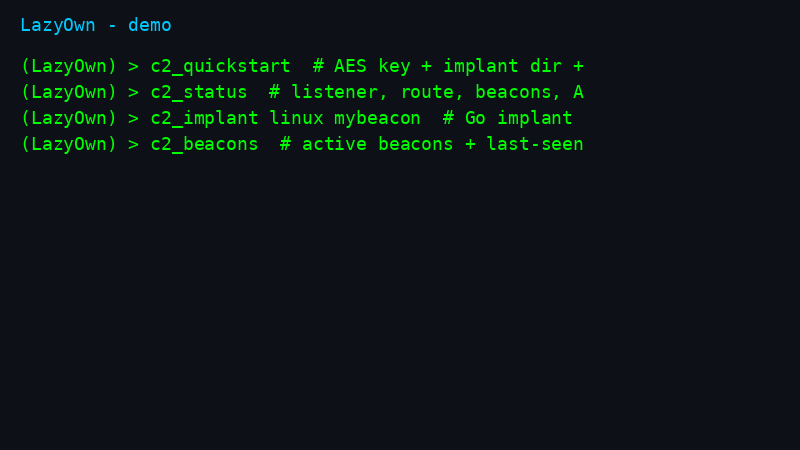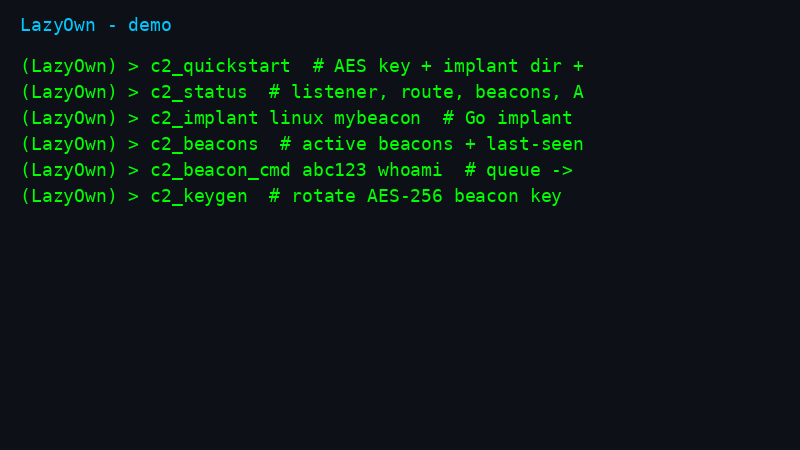 |  |
First victory in 5 minutes: TUTORIAL_5_MINUTES.md · Full walkthrough: QUICKSTART.md (5 min) · 80/20 guide: ESSENTIALS.md · HTB end-to-end: docs/examples/htb-lame-walkthrough.md · Honest comparison: COMPARISON.md
Doc
Automated by readmenator (pip install readminator)
https://grisuno.github.io/LazyOwn
<img width="1913" height="963" alt="image" src="https://github.com/user-attachments/assets/798fd75b-db6c-4443-a7bd-ed79788280ce" />Why LazyOwn vs Sliver / Havoc / Mythic / Caldera / Metasploit
| Capability | LazyOwn | Sliver | Havoc | Mythic | Caldera | Metasploit |
|---|---|---|---|---|---|---|
| Linux BOF support | yes | no | no | no | no | no |
| YARA + Nuclei marketplace built-in | yes | no | no | no | no | no |
| MCP server for AI agents (153 tools) | yes | no | no | no | no | no |
| LLM operator + multi-agent hive | yes | no | no | no | no | no |
| Multi-operator C2 + phishing engine | yes | partial | partial | partial | partial | partial |
Full table: COMPARISON.md. Found an error? Open an issue, we fix it.
 ██▓    ▄▄▄      ▒███████▒▓██   ██▓ ▒█████   █     █░███▄    █
▓██▒   ▒████▄    ▒ ▒ ▒ ▄▀░ ▒██  ██▒▒██▒  ██▒▓█░ █ ░█░██ ▀█   █
▒██░   ▒██  ▀█▄  ░ ▒ ▄▀▒░   ▒██ ██░▒██░  ██▒▒█░ █ ░█▓██  ▀█ ██▒
▒██░   ░██▄▄▄▄██   ▄▀▒   ░  ░ ▐██▓░▒██   ██░░█░ █ ░█▓██▒  ▐▌██▒
░██████▒▓█   ▓██▒▒███████▒  ░ ██▒▓░░ ████▓▒░░░██▒██▓▒██░   ▓██░
░ ▒░▓  ░▒▒   ▓▒█░░▒▒ ▓░▒░▒   ██▒▒▒ ░ ▒░▒░▒░ ░ ▓░▒ ▒ ░ ▒░   ▒ ▒
░ ░ ▒  ░ ▒   ▒▒ ░░░▒ ▒ ░ ▒ ▓██ ░▒░   ░ ▒ ▒░   ▒ ░ ░ ░ ░░   ░ ▒░
  ░ ░    ░   ▒   ░ ░ ░ ░ ░ ▒ ▒ ░░  ░ ░ ░ ▒    ░   ░    ░   ░ ░
    ░  ░     ░  ░  ░ ░     ░ ░         ░ ░      ░            ░
                 ░         ░ ░

LazyOwn comes with ABSOLUTELY NO WARRANTY. This is free software, and you are welcome to redistribute it under the terms of the GNU Affero General Public License v3. See the LICENSE file for details about using this software.
LazyOwn RedTeam Framework v 0.5.0
LazyOwn is a professional red team framework and Command & Control (C2) platform built for penetration testers, red teams, and security researchers. It delivers 872 CLI commands, 130 aliases, 153 MCP tools for AI agents, a multi-operator web C2 dashboard, and 137 YAML/Lua plugin integrations covering the full kill chain across Linux, Windows, macOS, and BSD.
New in this release: integrated marketplace with YARA rules + Nuclei templates, auto_loop autonomous exploitation, hunt command for threat-informed recon, post-command tips engine, automatic session data encryption, gamified ELO/badges, and 7 new APT playbooks. Plus: retry resume of interrupted chains/loops (with a guarded --sudo mode), chain_distill to turn one loop trace into a reusable chain YAML, typed verb manifests for the planner, and every installed lazyaddon surfacing as a toggleable addon:* verb.
Autonomous contracts update: the loop is now administered by
config/orchestrator.yaml profiles (default, stealth, lab, gym),
chains support conditions, timeouts, retries, capture and sink tags, and
every exploit, emulation step, chain result and finding fans out through
one outcome bus. Metasploitable 2 ships with 45 indexed vectors, one
exploit and one chain each, including SQLi, XSS, CSRF, LFI/RFI, upload and
command injection. Lazyaddons opt in to git fast-forward updates with
update: true; every shipped addon is opted in.
I also integrated autonomous-operation contracts into the existing
flows (safety gate and planner frontier inside the daemon loop,
provider failover, evidence vault, db-backed finding retests).
I verify them through the usual verbs. Full contract:
specs/autonomous_ops.md.
Quickstart in three commands
New here? This is the whole on-ramp. Full walkthrough: QUICKSTART.md.
Fastest path (one-liner: clones into ~/LazyOwn, installs, then asks whether
to start a normal ./run session or the full fast_run_as_r00t.sh stack):
curl -fsSL https://raw.githubusercontent.com/grisuno/LazyOwn/main/bootstrap.sh -o /tmp/bootstrap.sh \
  && bash /tmp/bootstrap.sh
(One-command alternative: curl -fsSL https://raw.githubusercontent.com/grisuno/LazyOwn/main/bootstrap.sh | bash.)
If ~/LazyOwn already exists, the installer asks whether to update in place, do a clean reinstall (backing up payload.json to /tmp first), use another directory, or abort.
Or step by step:
git clone https://github.com/grisuno/LazyOwn.git && cd LazyOwn
bash install.sh        # virtualenv + pinned dependencies + C2 certificates
./run                  # launches the shell; first run offers the setup wizard
The default install is light; add --with-ml for the heavy torch/CUDA stack, --with-ollama for the local LLM runtime, --with-tools for the common external binaries (forward them through the one-liner with bash -s -- <flags>). Dependencies are pinned in requirements.txt (cross-platform core) and requirements-ml.txt (optional ML); pyproject.toml is the single source of truth.
Docker
For isolated, reproducible engagements, see lazyown-docker/README.md.
cd lazyown-docker
./mkdocker.sh build
./mkdocker.sh run --vpn 1
Autonomous loop and chains
The generic golden path no lab, no containers, one authorized target:
lazy_loop --target 10.10.10.5 --rounds 6 "gain initial access"
apt_chain apt_generic 10.10.10.5              # auto-discovered fallback chain runs itself on failure
apt_chain apt_generic 10.10.10.5 --dry-run    # plan check only
# multi-target: one loop per line of scope.txt, max 3 in flight:
auto_loop --targets-from-file scope.txt --max-concurrent 3 "gain initial access"
apt_chain is self-recovering by schema: steps accept
pre_check (skip the step early when a cheap predictor fails), steps
accept parallel: true (independent scans run concurrently), and
chains accept fallback: <chain> (a failed chain re-runs its fallback
with the same run id, reported as fallback_used). Repeated failures
can hand the objective to the model: apt_chain ... --replan.
Contract: docs/autonomous-loop.md.
The loop reads config/orchestrator.yaml; explicit flags still win.
lazy_loop --profile gym --target 172.17.0.2 "root the gym"
apt_chain gym_metasploitable_ms2_distcc_exec 172.17.0.2
apt_chain gym_metasploitable_ms2_distcc_exec 172.17.0.2 --dry-run
# something failed mid-chain? resume only what did not finish:
retry status
retry chain gym_metasploitable_ms2_distcc_exec --var target=172.17.0.2
retry chain gym_metasploitable_ms2_distcc_exec --sudo   # guarded: prints a warning, waits for YES
# distill a finished loop trace into a reusable chain:
chain_distill t0001 --write
# choose what the loop may run (837 shell verbs + every lazyaddon):
verb list addon
verb on addon:adcs_attacks
gym_ms2 list
gym_ms2 validate
lazy_addon update --all --dry-run
lab start metasploitable prints the container IP and the assign rhost
line, starts Apache when the image boots without it, and applies the gym
migrations automatically (modules/metasploitable_migrations.py): core
daemons, telnet/rlogin/rsh access from the docker subnet, anonymous FTP,
an open X display, the Shellshock CGI, the mutillidae database (setup +
mirror into metasploit) and the canonical DVWA DOM XSS page. Three
vectors need extra cheerleading inside a container, and migrations fix
them too: a Python DNS responder stands in for bind9 (Docker strips the
capset it wants), a userspace rpc.mountd stands in for the kernel
NFS server, and /root/.rhosts trusts the loopback for rsh. All 45
shipped vectors yield a shell on the lab. Setup guide:
docs/gym-setup.md.
The outcome bus updates the world model, kill-chain, intel graph, attack
graph, C2 banners/CVEs/notes, objectives and session report from one
event. Contracts: docs/autonomous-loop.md,
docs/outcome-bus.md,
docs/emulation-runner.md,
docs/metasploitable-gym.md.
Then, inside the (LazyOwn) > shell:
doctor          # preflight: verifies Python, venv, packages, certs, SecLists, tools
wizard          # guided config (auto-detects lhost, walks 8 steps incl. LLM provider)
ping            # confirm the target is up and detect its OS
lazynmap        # full port + service scan
If doctor reports a blocking failure (red), fix it before going further it
tells you the exact pip install / apt install command for whatever is
missing. Warnings (yellow) are optional features you can ignore for now.
Autonomous loop
LazyOwn ships a native autonomous loop: one command drives a full
engagement round by round (scope, enrichment, planning, workers, guard,
traffic, findings, retest, compaction, intel fusion, report), with every
step persisted and auditable under sessions/lazy/.
auto_loop --target 10.10.10.5 --rounds 6 --workers 2 "gain initial access"
lazy_loop --view            # resume/observe with the live worker monitor
lazy_view t0001             # attach the monitor from another terminal
lazy_orchestrator           # admin console: stages, verbs, playbooks, gyms, chains, profiles, LLM chain, guard
Highlights:
- configurable pipeline: enable/disable each stage and manage the auto
verb registry (
lazy_orchestratorPipeline and Verbs tabs, with a searchable command picker when adding verbs); - playbook administration: list, preview, create, edit and delete
playbooks/*.yamlfrom thelazy_orchestratorPlaybooks tab; - gym administration: YAML definitions under
gyms/, persistent runs in the world model, and alazy_orchestratorGyms tab to start/stop them; - transparent execution: every step is narrated live, with heartbeats, a stall watchdog and thread-stack dumps when nothing moves;
- safe teardown:
Ctrl+C,qa,exit, EOF andatexitkill children, close shell sessions, pause tasks and leave everything resumable; - intel fusion: each round merges logs into the world model, findings
lifecycle and objectives via
lazy_bridge.sync_all.
Full documentation: docs/autonomous-loop.md.
Core Architecture
LazyOwn is built around a modular, command-driven architecture that provides flexibility and extensibility for security testing workflows.
LazyOwn Skills MCP Integration
Connect AI agents to the framework via the Model Context Protocol (MCP). The MCP server
(skills/lazyown_mcp.py) exposes 0 tools covering the full engagement lifecycle.
bash scripts/setup_hermes_mcp.sh # register the MCP server
Then restart your agent or run /reload-mcp. Full tool playbook: skills/lazyown.md.
Agent setup details (Claude Code, Hermes, OpenCode, env vars, tool groups): docs/mcp-setup.md.
Key Features
- 872 Attack Commands: Full kill-chain coverage across Linux, Windows, macOS, and BSD recon, enum, exploit, privesc, lateral movement, credential access, C2, exfiltration, and reporting.
- Interactive cmd2 CLI: Fuzzy autocomplete, neon-box configurable prompt, command palette (
Ctrl+K), inline reactive hints after every command, and a Textual TUI dashboard. - Integrated Marketplace:
yara_marketplace(10 built-in rules: ransomware, C2, webshells, obfuscation, privesc),nuclei_marketplace(500+ templates),marketplacefor community plugins/addons all browsable via curses TUI. - auto_pwn & hunt: Autonomous exploitation chaining and threat-informed recon
auto_pwnwalks kill-chain phases automatically,huntexecutes targeted discovery based on known TTPs. - Unified Post-Command Tips Engine: Smart suggestions (kill-chain hints, protips, curiosity, autosuggest) with ELO rating, badges (First Blood, Arsenal Master, Kill Chain Master), and VRI rewards gamified operator experience.
- Automatic Session Crypto:
auto_cryptoencrypts sensitive session files on exit and decrypts on startup (PBKDF2HMAC + Fernet), transparent to the operator. - AI-Native Architecture: MoE (Mixture of Experts) router, RL training, SWAN orchestrator, Hive Mind multi-agent system, ACI (Autonomous Campaign Intelligence) planner the first C2 that plans, executes, and learns autonomously.
- Multi-Stage Obfuscated Go Implants: Two-stage XOR-encoded beacon delivery with C stubs, AES-256 encrypted C2 channels, VM/sandbox/debugger evasion, polymorphism, and LOLBAS-based stagers. Tested on Kernel 6.12 and Windows 10.0.20348.
- Linux BOF (Beacon Object Files): First open-source C2 framework with BOF support for Linux via ELF
dlopenruntime. Source-compatibledatapAPI with Windows BOF contract. Direct syscalls andio_uringsupport. - Decoy Blue Team Trap: Flask decoy website records video/audio and captures images of unauthorized visitors (blue team operators probing the C2), stored in
sessions/captured_images. - Bloodhound Attack Surface: Upload Bloodhound ZIP data to render interactive attack surface graphs with filtering and search, augmented by
lazynmapdiscovery data. - AI-Powered Phishing Engine: Groq/DeepSeek AI-generated email templates with dynamic URL generation, tracking pixels, URL shortening, and test endpoint creation.
- Decoy: if the ip addres not match with 127.0.0.1 or lhost flask will show a decoy website this decoy site will record a video with audio and take pictures from the intruder (sessions/captured_images) like a small versión of storm breaker to know who is the blueteam operator
- Adversary Simulation: Advanced capabilities for generating red team operation sessions, ensuring meticulous and effective simulations.
- Task Scheduling: Utilize the
croncommand to schedule and automate tasks, enabling persistent threat simulations. - Real-Time Results: Obtain immediate feedback and results from security assessments, ensuring timely and accurate insights.
- RAT and Botnet Capabilities: Includes features for remote access and control, allowing for the management of botnets and persistent threats.
- C2 Framework IA Powered: Acts as a command and control (C2) framework, enabling covert communication and control over compromised systems. and many IA bots to improve your opsec, Developed in Flask, providing a user-friendly interface for seamless interaction. Now with network discovery capabilities, allowing us to see the attack surface on our client map clearly and intuitively with filters and a search panel. New functionalities are coming soon.
- C2 LazyAddon Creator: Guided
/addonspages in the C2 dashboard to authorlazyaddons/*.yamlintegrations without touching YAML by hand. One form exposes every addon option (name, description, author, version, enabled, target OS, trigger services, category, module type, install type, parameters, tool block, C2 extras, environment variables) with tooltips, placeholders, and per-field help. Placeholder chips ({rhost},{url}, declared params, and every payload.json key) are drag-and-drop into command boxes. Server-side validation rejects unsafe names, path traversal, unknown placeholders, and malformed URLs before the file is written; writes are atomic and secure (temp file created with restrictive permissions viamkstemp+fchmod, flushed and fsynced, then promoted withos.replace). The list and YAML preview pages complete the lifecycle. Every mutating route is CSRF-protected. Contract:lazyc2/addon_creator.py+lazyc2/blueprints/addons.py, covered bytests/test_addon_creator.pyand thetests/run_mutation_addon_creator.pymutation gate.
- Undetectable, Obfuscated, and Malleable GO Implants: The command with the payload comes obfuscated by default. Instead of directly downloading the beacon, it downloads a stub created in C to download the beacon, which is XOR-encoded with a key. It is then decoded in memory and executed in a temporary path with a unique name to evade detection, using svchost in Windows and lazyservice in Linux. This performs a two-stage implant, which has been tested on Kernel 6.12 and Windows [Version 10.0.20348.3807]. Additionally, an alternative Windows stub using LOLBAS PS1 and Csharp has been added, along with a version of ebird3 in LOLBAS that uses the same technologies. The Go beacon is a multi-platform, undetectable, and highly obfuscated implant tailored for advanced red teaming operations. It features polymorphism, operates in a configurable stealth mode, and secures communications with AES-256 encrypted channels. The beacon blends into environments by simulating legitimate network traffic and evades detection by identifying virtual machines, sandboxes, containers, and debuggers, dynamically adjusting its behavior. With a minimal footprint, it supports robust network discovery through ping-based host enumeration and port scanning of configured targets. The implant excels at exfiltrating sensitive data, including private keys, AWS credentials, browser credentials, and system logs. It offers dynamic TCP proxying for traffic redirection, privilege escalation attempts, and system log cleaning. Persistence is achieved across Windows, Linux, and macOS via scheduled tasks, systemd, crontab, and LaunchAgents. Additional capabilities include adversary emulation (MITRE ATT&CK), file timestamp obfuscation, and directory compression for exfiltration. Built with Go vet for code health, the implant integrates seamlessly with Dockerized environments and AWS Firecracker microVMs, making it a cornerstone of modern red team infrastructure, Built with Go vet for code integrity, the implant leverages Cloudflare for traffic obfuscation, routing communications through secure, high-performance redirectors to conceal C2 infrastructure. The Go binary is hardened with Garble obfuscation, thwarting reverse engineering and signature-based detection. On Windows, the implant employs extension camouflage to masquerade as benign files (e.g.,
.pdfx) and embeds custom icons viarsrcfor convincing social engineering.
Available beacon commands:
- stealth_off stop being stealthy, Disables stealth mode, allowing normal operations.
- stealth_on enter ninja mode, Enables stealth mode, minimizing activity to avoid detection.
- download: download:[filename] Downloads a file from the C2 to the compromised host.
- upload: [filename]: Uploads a file from the compromised host to the C2.
- rev: Establishes a reverse shell to the C2 using the configured port.
- exfil: Exfiltrates sensitive data (e.g., SSH keys, AWS credentials, command histories).
- download_exec: download_exec:[url]: Downloads and executes a binary from a URL (Linux only, stored in /dev/shm).
- obfuscate: [filename]: Obfuscates file timestamps to hinder forensic analysis.
- cleanlogs: Clears system logs (e.g., /var/log/syslog on Linux, event logs on Windows).
- discover: Performs network discovery, identifying live hosts via ping.
- adversary:[id_atomic]: Executes an adversary emulation test (MITRE ATT&CK) using downloaded atomic redteam framework scripts.
- softenum: Enumerates useful software on the host (e.g., docker, nc, python).
- netconfig: Captures and exfiltrates network configuration (e.g., ipconfig on Windows, ifconfig on Linux).
- escalatelin: Attempts privilege escalation on Linux (e.g., via sudo -n or SUID binaries).
- proxy:[listenip]:[listenport]:[targetip]:[targetport] Starts a TCP proxy redirecting traffic from listenAddr to targetAddr.
- stop_proxy:[listenaddr] Stops a TCP proxy on the specified address.
- portscan: Scans ports on discovered hosts and the configured rhost.
- compressdir:[directory]: Compresses a directory into a .tar.gz file and exfiltrates it.
- sandbox: Get info about the system if it's a sandbox or not.
- isvm: Get info about the system if it's a virtual machine or not.
- debug: Get info about the system if the target is debugged or not.
- persist: Try to persist mechanism in the target system.
Command Capabilities
LazyOwn provides 872 commands across 13 kill-chain phases, available from both CLI and web C2 dashboard:
| Phase | Highlight Commands |
|---|---|
| Recon | lazynmap, ping, whatweb, gobuster, ffuf, dig, dnsenum, finalrecon |
| Enum | enum4linux, cme, bloodhound, nuclei, kerbrute, ldapdomaindump |
| Exploit | auto_pwn, hunt, ss (searchsploit), venom, lazymsfvenom, searchhash |
| Post-Exploit | linpeas, winpeas, blacksandbeacon, mimikatzpy, disableav |
| Persistence | persist, backdoor, cron, schtask, createwebshell |
| PrivEsc | getcap, sudo, adcs_check, privesc_predictor |
| Cred Access | secretsdump, evil, getnpusers, hashcat, john, spraykatz |
| Lateral | psexec, wmiexec, ssh_cmd, chisel, ligolo, bloodhound |
| Exfil | exfil, upload_gofile, encrypt/decrypt, compressdir |
| C2 | lazyc2, blacksandbeacon, createrevshell, listener_go |
| Reporting | report, lazyreport, campaign_sitrep, timeline, dashboard |
| AI/Agents | auto_loop, recommend_next, playbook_generate, playbook_run, orchestrate |
| Marketplace | yara_marketplace, nuclei_marketplace, marketplace, lab |
Core management: assign, show, doctor, wizard, scope, collab_join, config_banner, palette, fz.
See COMMANDS.md for the full 872-command reference and ESSENTIALS.md for the 18 commands that cover 80% of engagements.
Go deeper
| Guide | Contents |
|---|---|
docs/collaboration.md | Multi-operator C2: SSE stream, publish, target locks |
docs/autonomous-loop.md | Autonomous loop: pipeline stages, auto verbs, observability, audit, teardown, retry/resume, chain distillation, verb catalog |
docs/command_chain.md | prev/next: what runs before and after a verb |
docs/metasploitable-gym.md | Gym: 45 indexed MS2 vectors, migrations, verified matrix |
docs/lab-gym-toolkit.md | AD Docker gym, self-healing WinBox gym, gym auto-chain, lab scope guard, lazycreds KB, lazyoob canary, web playbook, kerninc addon |
docs/browser-sync.md | Real browser session into the proxy: cookie extension, receiver, identity injection, Match and Replace rules |
docs/mcp-setup.md | MCP setup per agent, env vars, 153 tool groups |
docs/cli-ux.md | Audit mode, fuzzy autocomplete, prompt themes, palette, dashboard |
docs/ai-architecture.md | MoE router, RL trainer, SWAN, Hive Mind, detection oracle |
docs/operator-safeguards.md | Scope guard, reproducible installs |
docs/profiles.md | Install profiles: full vs light (LAZYOWN_PROFILE) |
docs/lua-plugins.md | Write Lua plugins for the shell |
docs/lazyaddons-yaml.md | Author YAML tool integrations |
docs/telegram-bot.md | Telegram Hermes C2 bot setup |
docs/beacons-linux-bof.md | Linux BOF beacon: build, deliver, port from Windows |
docs/related-projects.md | Related beacons, C2s, and tooling |
Full references (auto-generated, standalone)
COMMANDS.mdfull 872-command referenceUTILS.mdhelper-function reference forutils.pyCHANGELOG.mdrelease history
Media
- YouTube, podcast, and DeepWiki links live with the launch kit:
docs/launch_kit/POSTS.md
License
LazyOwn is free software under the GNU General Public License v3 see LICENSE. Comes with ABSOLUTELY NO WARRANTY.
Acknowledgments
A special thanks to GTFOBins for the valuable information they provide and to you for using this project. Also, thanks for your support Tito S4vitar! who does an extraordinary job of outreach. Of course, I use the extractPorts function in my .zshrc :D, thanks to deepwiki to help us with doc. ( https://deepwiki.com/grisuno/LazyOwn/ ), thanks to plaintext who does an extraordinary job of outreach and we adopted PTMultiTools it's very impresive
Thanks to pwntomate
An excellent tool that I adapted a bit to work with the project; all credits go to its author honze-net Andreas Hontzia. Visit and show love to the project: https://github.com/honze-net/pwntomate
Thanks to Sicat
An excellent tool for CVE detection, I implemented only the keyword search as I had to change some libraries. Soon also for XML generated by nmap :) Total thanks to justakazh. https://github.com/justakazh/sicat/
Thanks to josefcohernandez
For identifying and reporting the Docker build failures caused by the repo.charm.sh outage and the Python version incompatibility. His report led to the fixes in lazyown-docker/Dockerfile.
Thanks to EQSTLab (via yym8538)
For two critical security advisories that helped us harden the framework and fix serious vulnerabilities. Their responsible disclosure makes LazyOwn safer for the entire community.
KitPloit.com
We, the people who dedicate time to LazyOwn, are flattered by that excellent review on Kitploit. Thank you so much, it helps us reach a wider community.
- https://kitploit.com/es/tools/github/grisuno/lazyown
- https://kitploit.com/en/tools/github/grisuno/blacksandbeacon
- kitploit.com/en/tools/github/grisuno/cve-2022-22077
Spook.news
Thank you so much, Spooky News members! It's an honor to be recommended by you. Thank you so much! https://spook.news/members/stipko_news_pv.php?id=65519
Vulners.com
Thank you so much, Vulners! All publicity is good publicity, and we will strive to improve. https://vulners.com/kitploit/KITPLOIT:TOOLS-GITHUB-GRISUNO-LAZYOWN
Bharat Kayth
We love your post bro :D Thank you so much. https://www.linkedin.com/posts/splog_lazyown-is-a-comprehensive-red-team-framework-share-7445191628039974912-viWM/
cmd2
Thanks to cmd2 for making this tool possible through their great work, and we love being recommended as a good example of tools made with cmd2, we are honored. https://pypi.org/project/cmd2/
ZONE.CI 全球网
Many thanks to ZONE.CI for their review, but they failed to check some repositories before confirming that we're missing capabilities announced in the readme. They're not in the repo, but they load as lazy add-ons ;) blacksandbeacon event kiploit known win beacon
CN-Sec was wrong to say that these techniques "were not implemented." Hacktricks (https://hacktricks.wiki/en/linux-hardening/post-exploitation/linux-fileless-execution.html ), one of the most respected sources in offensive security, includes LazyOwn as an official reference for:
- Fileless post-exploitation techniques in Linux
- Linux BOF implementation with .so/dlopen
- Memory staging (runtime decoding/decompression)
- Deleted-file execution
https://zone.ci/secarticles/wx/587776.html
mcpharbor.app
Many thanks to mcpharbor.app for adding the lazyown mcp to their list of tools; we are honored to be featured on their website. https://mcpharbor.app/tools/grisuno-lazyown/
Verified Skill
We are proud that our humble skill has been verified in verified skills, it gives us a lot of encouragement to continue developing this lovely community. https://verified-skill.com/skills/grisuno/lazyown/lazyown?utm_source=lazyown_redteam
CN-Sec
Some echoes of Zone.ci, in any case we appreciate their words, they were not in vain and we have not only mitigated a large part of what was mentioned, if not all, and we will continue to improve day by day. https://cn-sec.com/archives/5401000.html
Awesome bof
Thank you so much for your work compiling bofs, it's incredible! We are proud to be indexed in your magnificent list https://chryzsh.github.io/awesome-bof/site/
LibHunt
Great comparison! We love that the community does these benchmarks so that at the end of the day each operator can choose the best option. Thank you very much, LibHunt. https://www.libhunt.com/compare-LazyOwn-vs-tor-rootkit
Hacktricks
Honestly, the team is speechless, and I think I speak for everyone when I say that when I started, I was reading everything on Hacktricks, and now being on one of their pages fills us with love. Thank you so much, Hacktricks, for your amazing work! https://hacktricks.wiki/en/linux-hardening/post-exploitation/linux-fileless-execution.html
Star History
<a href="https://www.star-history.com/#grisuno/LazyOwn&Date"> <picture> <source media="(prefers-color-scheme: dark)" srcset="https://api.star-history.com/svg?repos=grisuno/LazyOwn&type=Date&theme=dark" /> <source media="(prefers-color-scheme: light)" srcset="https://api.star-history.com/svg?repos=grisuno/LazyOwn&type=Date" /> <img alt="Star History Chart" src="https://api.star-history.com/svg?repos=grisuno/LazyOwn&type=Date" /> </picture> </a> <!-- readmenator-kb-link -->Knowledge Base
This project has been analyzed by ReadMenator,
a zero-token polyglot static analysis tool. Regenerate with
pip install readmenator && readmenator . --rebuild. Analysis outputs:
- KNOWLEDGE_BASE.md -- Full architecture reference with all classes, functions, imports, dependency graphs, UML class diagrams, security audit findings, community analysis, taint paths, hotspots, cycles, and more.
- readmenator-agent/ -- Agent-friendly, grep-optimized index.
INDEX.md-- Quick reference: what each file doesSYMBOLS.md-- Every symbol with file:lineARCHITECTURE.md-- Internal dependency pairs + external importsAPI.md-- Public function contractsGOTCHAS.md-- Change warnings (blast radius, cycles, hotspots)SECURITY.md-- Findings by severity with fix hintsMEMORY.md-- Rules, workflow, style, deliverables, session logMANIFEST.json-- Freshness (git_commit + source_fingerprint) + read orderKB_<subsystem>.md-- Per-subsystem contextrecipes/*.md-- Grounded task guides (add-function, fix-cycle, ...)
- readmenator-wiki/ -- Navigable wiki (start here for the big picture).
index.md-- Entry point: overview, reading order, god nodes, connectionscommunity_*.md-- One synthesis page per code communityconnections.json-- Typed bridges between communitiesqueries.md-- Suggested questions + answer logREPORT.md-- Honest audit: coverage, confidence, limits
- readmenator-graphrag/ -- Zero-token GraphRAG index.
index.json+REPORTS.md-- Query withreadmenator . ask "<question>"
- readmenator-apidocs/ -- API reference (Sphinx/Doxygen style).
index.md+modules/*.md-- Signatures, parameters, returns, raises, examples, call graphsarchitecture.md-- Tiered architecture + execution flows (control flow, call tree, sequence)classes.md,genindex.md,COVERAGE.md-- Hierarchy, A-Z index, doc coverage + warningsindex.html+api/-- Offline searchable browser and machine-readable model (api/index.json,api/modules/*.jsonlone entity per line)
- readmenator-maps/ -- Interactive gallery (
index.html).- 5 system maps: architecture, workflow, sequence, dataflow, lifecycle
graph-force.html-- Force-graph explorer (2D/3D, reach, paths, lenses)graph-bundle.html-- Edge bundle explorer (circle + sphere)components.html-- Component diagrams
- docs/ -- Static site (GitHub Pages ready).
- Gallery copy +
llms.txt(agent entry point) +md/docs + video
- Gallery copy +
- readmenator-diagrams/ -- Component diagrams.
analysis.json+graph LRmarkdown + per-component pages +index.html
- readmenator-rules/ -- Suggested Semgrep rules (
*.yml),yara_rules.yar(YARA-lite) +exclusions.yaml(false-positive blocklist) - readmenator.mp4 -- Cinematic synthwave overview video
- .cursorrules -- Generated AI assistant rules
- readmenator_audit.sarif -- SARIF v2.1.0 audit (when security scan is on)
Cache (.readmenator_cache/), packaged agent skills (.claude/skills/), and the
GitHub wiki mirror are also produced on run/--rebuild.
AI agents: Read readmenator-wiki/index.md first for the big picture, then readmenator-agent/INDEX.md for grep-friendly lookup.
Developers: Read KNOWLEDGE_BASE.md for full architecture reference, open readmenator-maps/index.html for the visual gallery.
Deployed with deploynator
<!-- /deploynator-footer -->LazyOwn alternatives
View more →Similar mcp servers in Developer Tools, ranked by GitHub stars. Compare licence, recent activity and scan status before you choose.
| Name | Stars | Licence | Last updated | Scan |
|---|---|---|---|---|
| LazyOwn (this page) grisuno | 300 | AGPL-3.0 | Nov 1, 2026 | Scanned, no flagged issues |
| MCP Use mcp-use | 11k | MIT | Oct 30, 2026 | Scanned, no flagged issues |
| MobileBuildMCP getsentry | 6.5k | MIT | Nov 1, 2026 | Scanned, no flagged issues |
| Gemini Notebook MCP CLI jacob-bd | 6.4k | MIT | Oct 27, 2026 | Scanned, no flagged issues |
| Mcporter openclaw | 5.1k | MIT | Oct 27, 2026 | Scanned, no flagged issues |
| Flint Chart microsoft | 4.5k | MIT | Nov 1, 2026 | Scanned, no flagged issues |